The EU AI Act, mapped to your codebase
Scanara is for teams that build or deploy AI systems in the EU. It scans your code in 10+ programming languages and your documents in 8 EU languages. Each finding names the EU AI Act article behind it, so you know what to fix. Scanara also drafts your compliance dossier for review by your legal team.
- Rules generated from the Regulation’s text
- 66 of 113 articles with automated rules (24 Aug 2026)
- Every finding cites its EU AI Act article
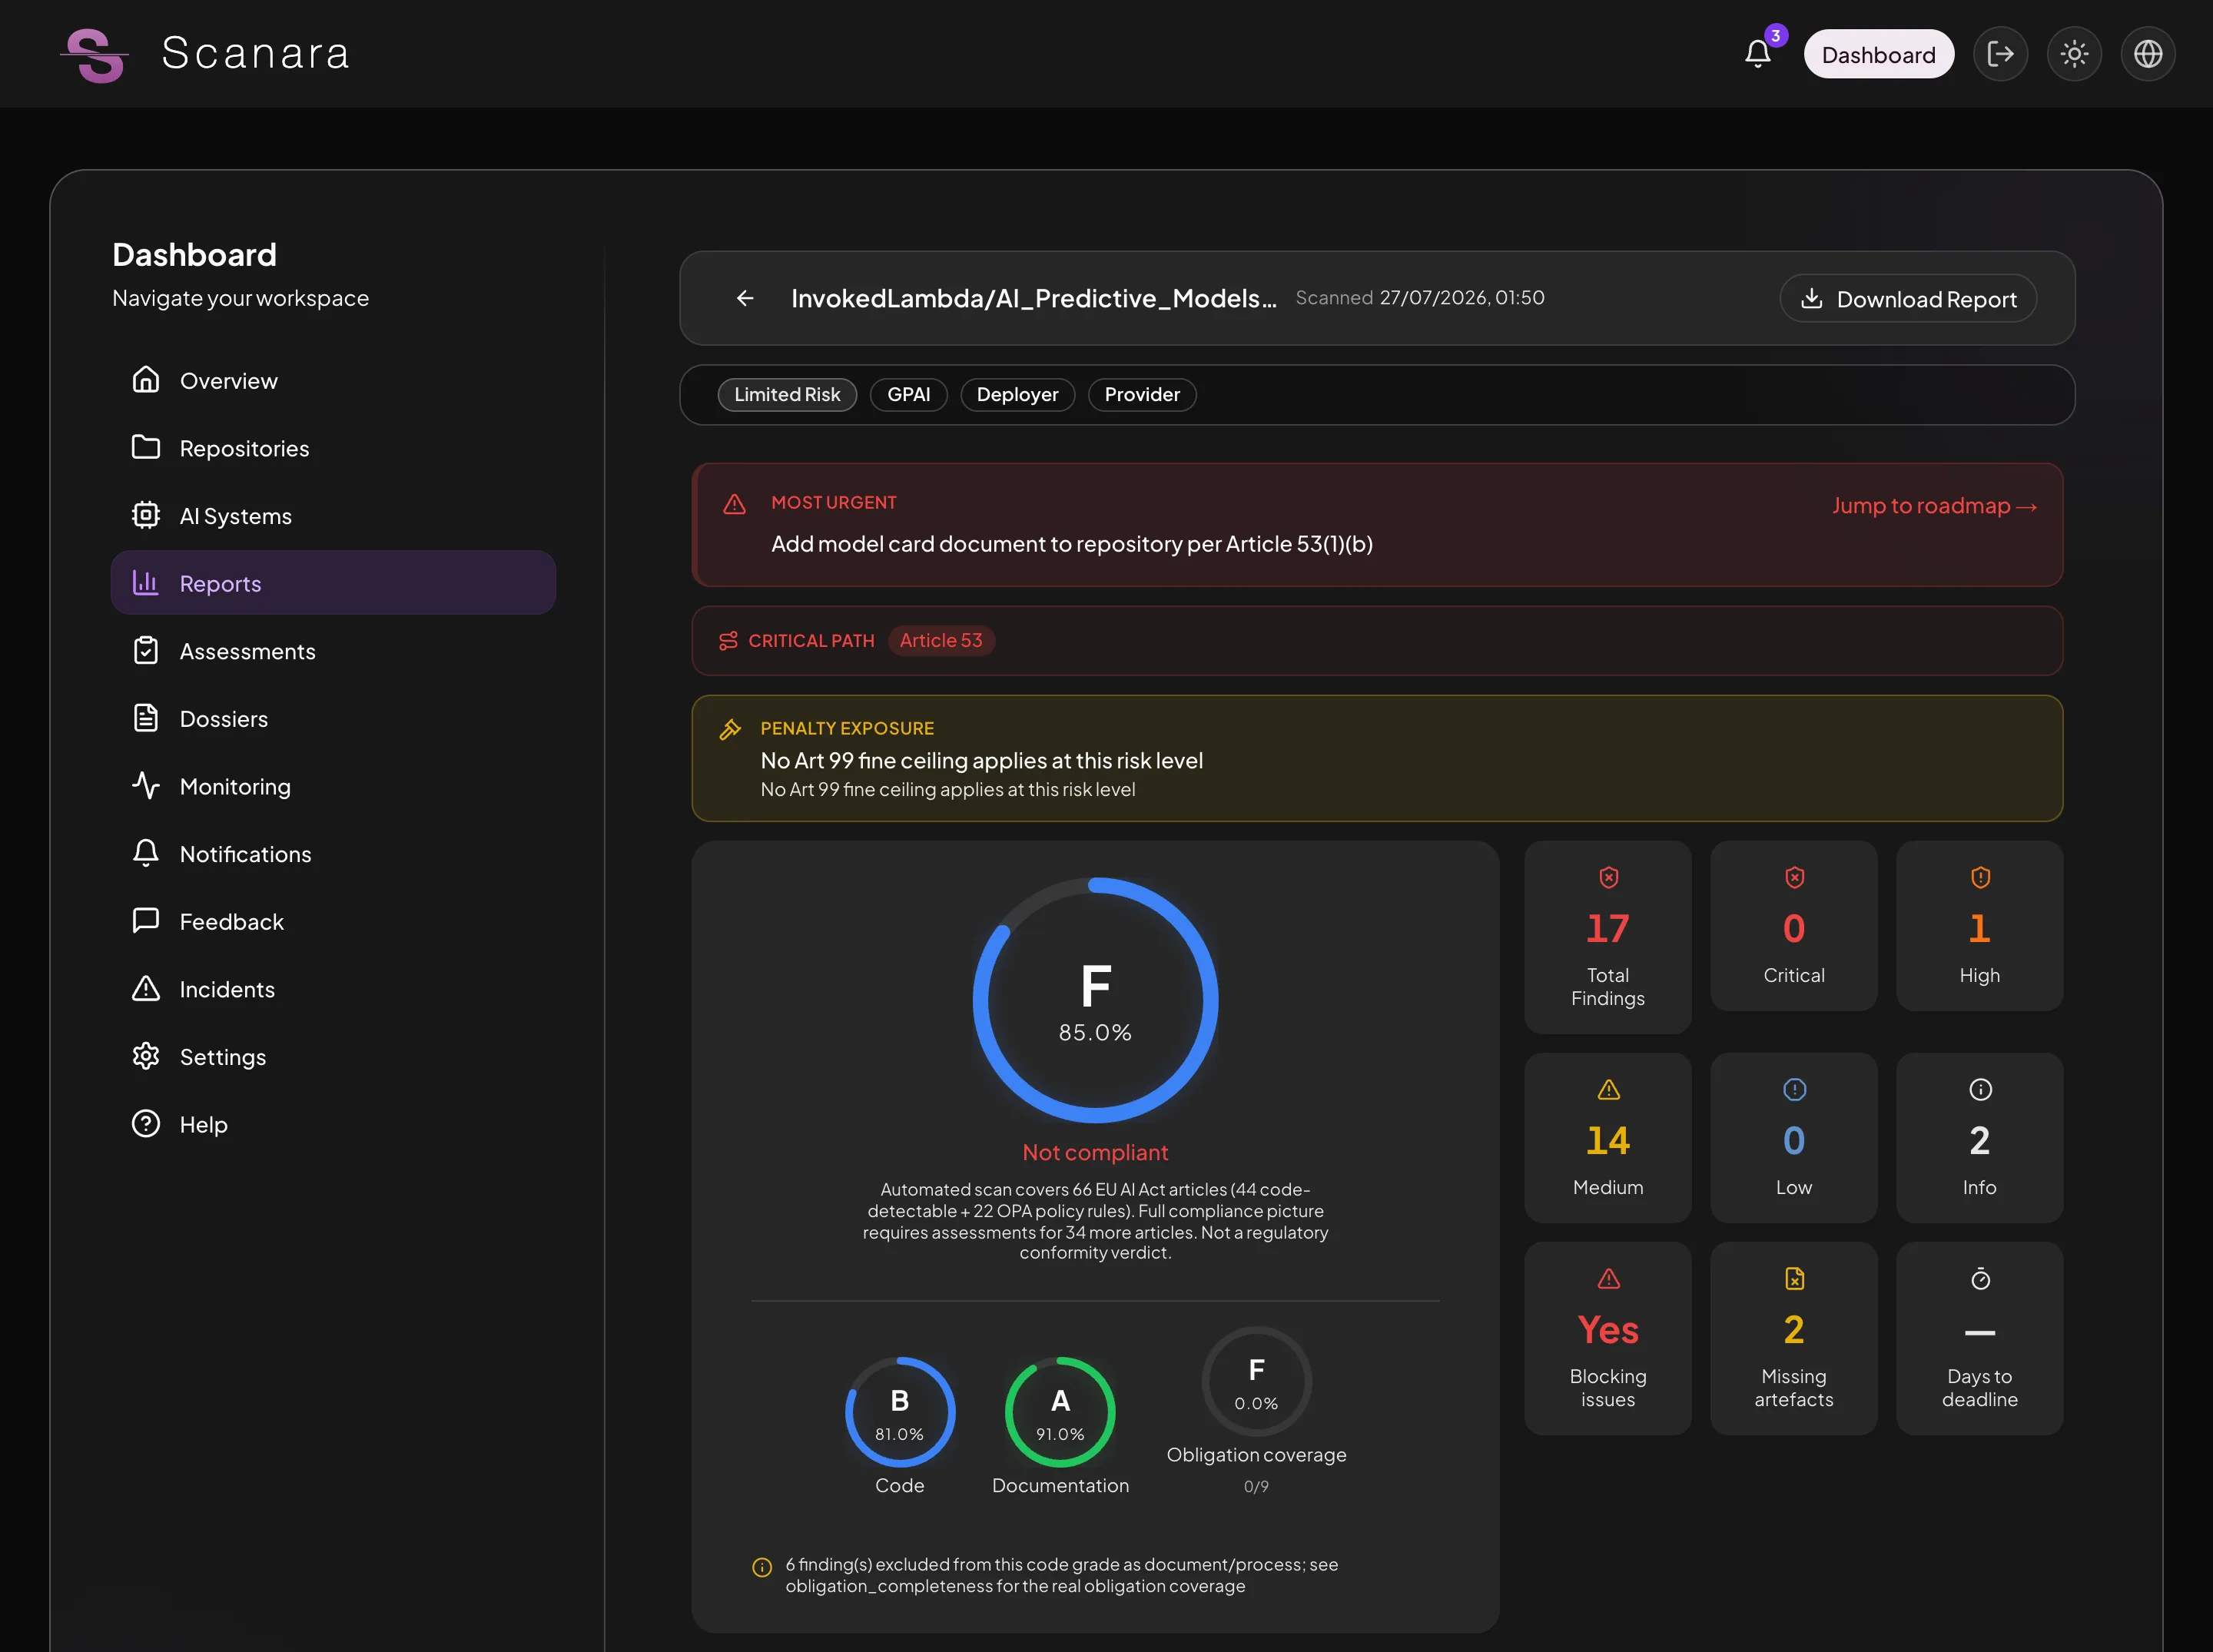
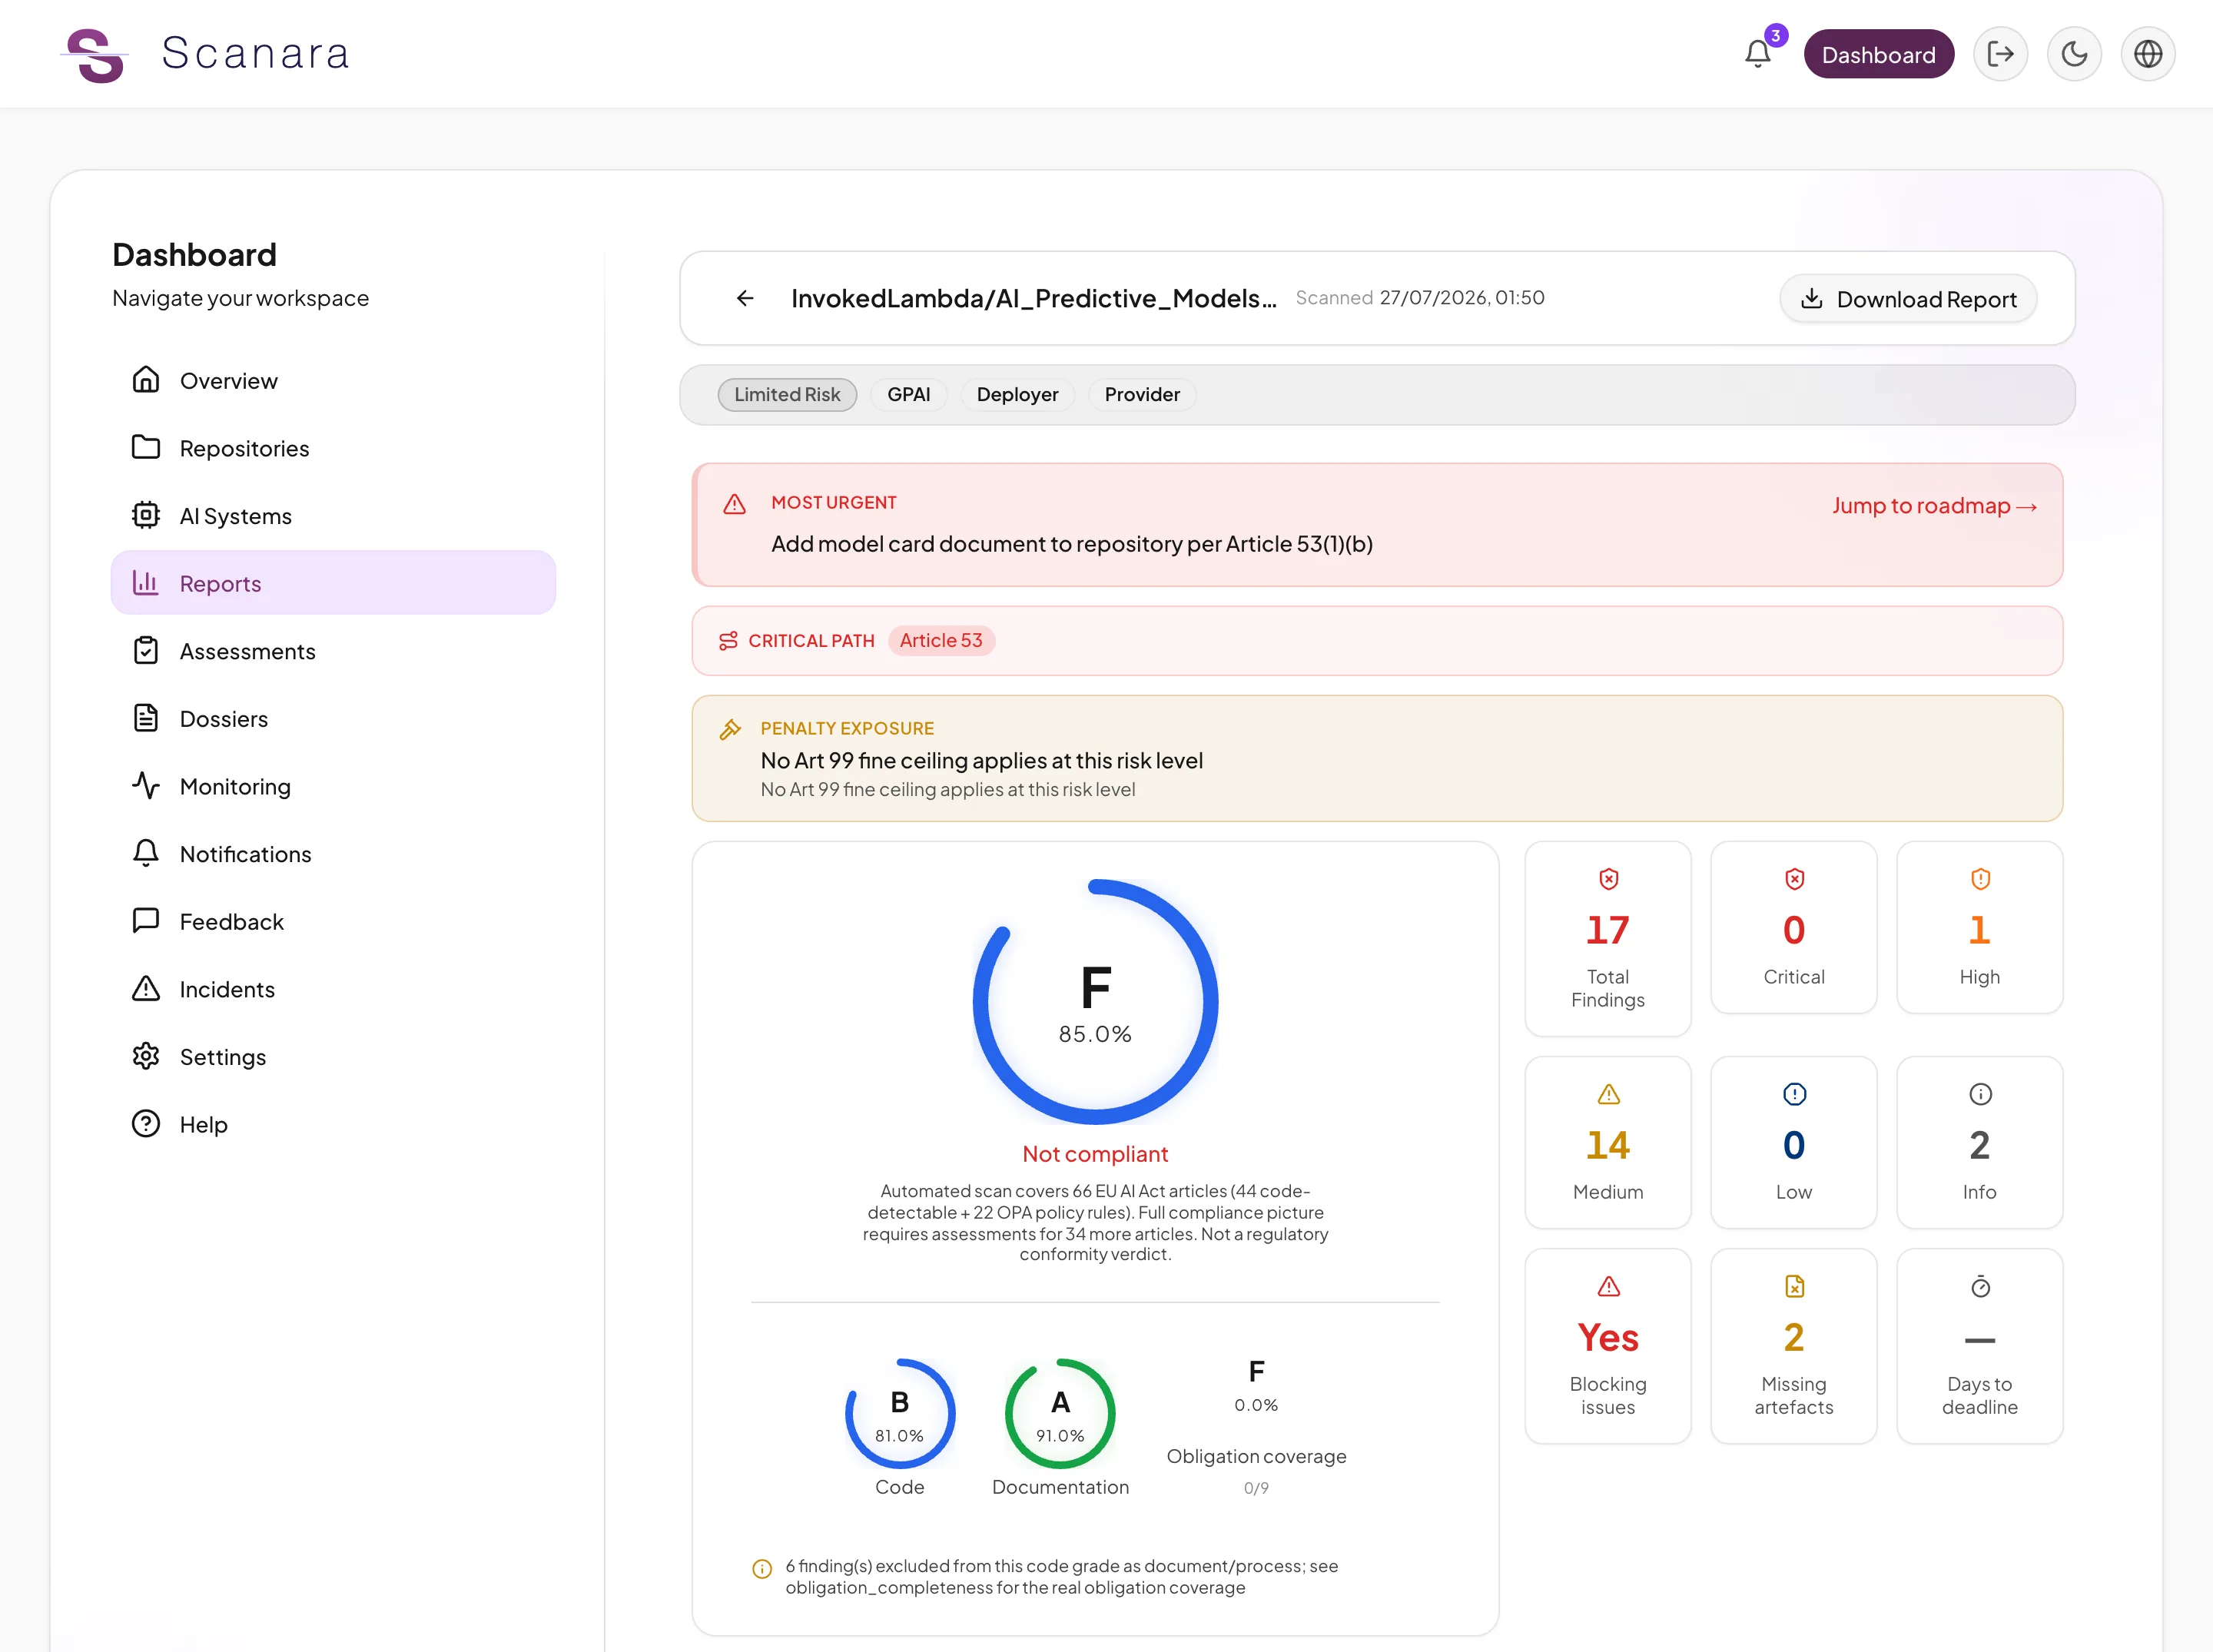
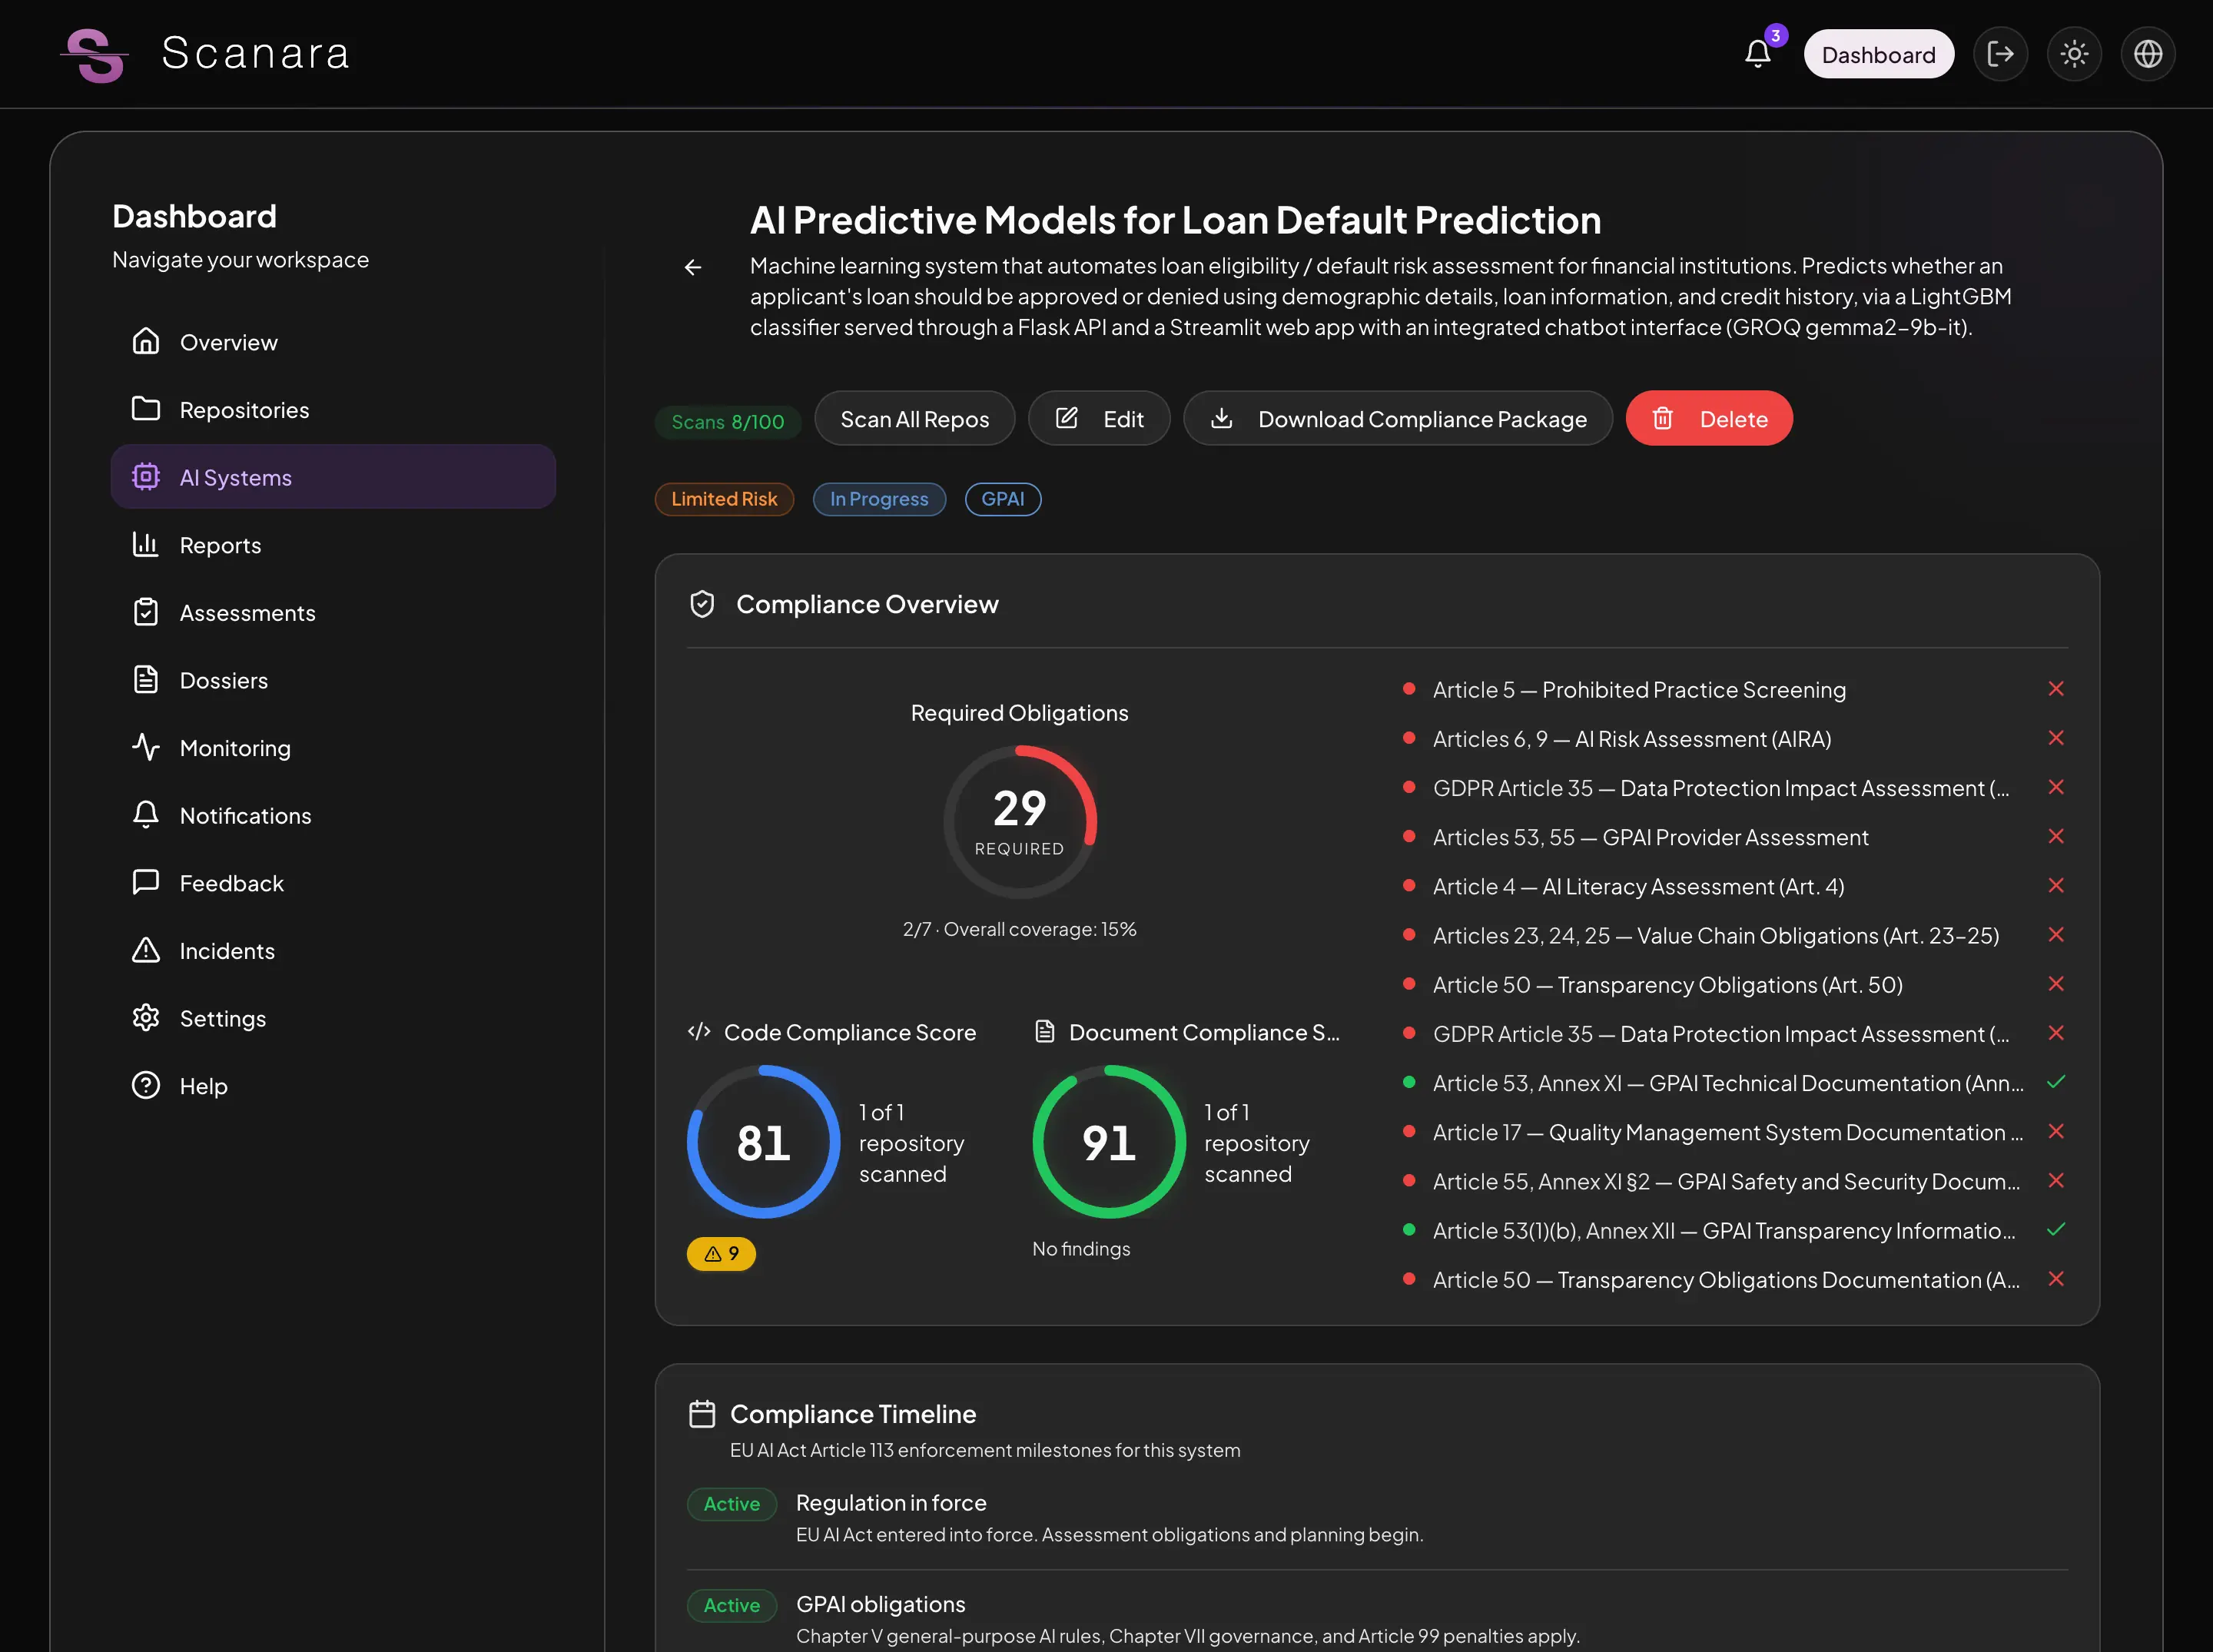
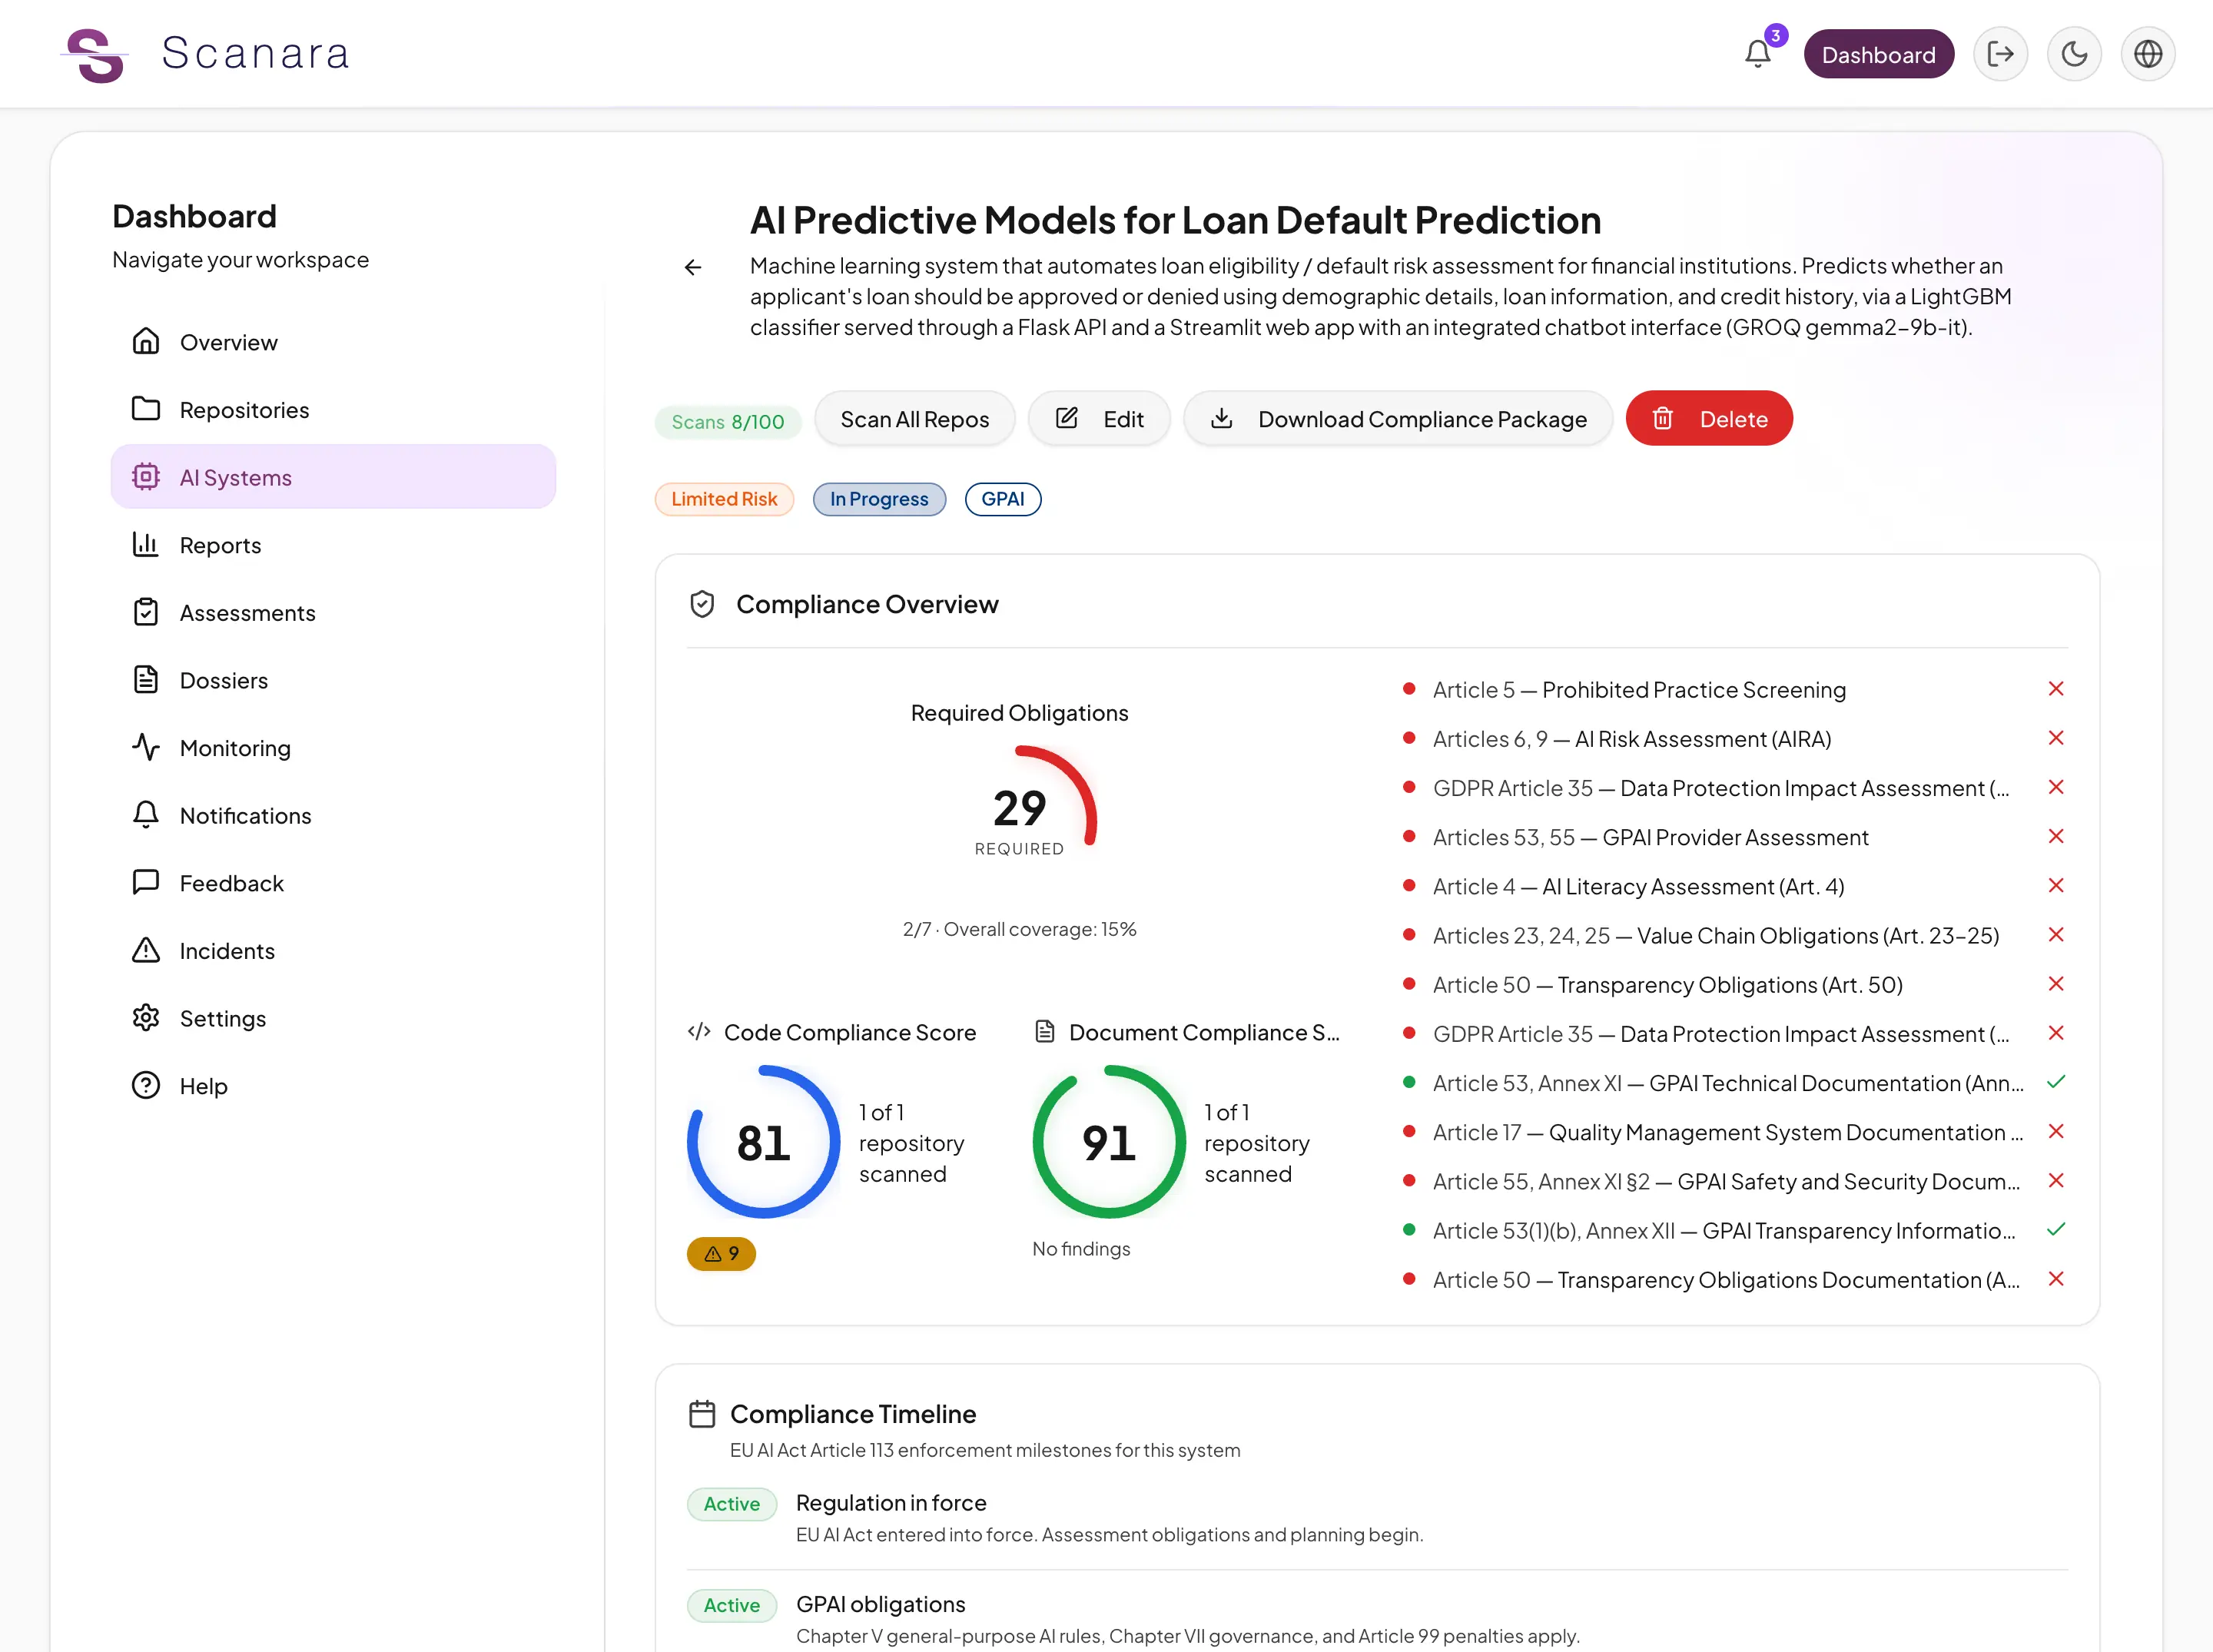
Example scan: open-source loan-default prediction model (limited risk, GPAI obligations)
The EU AI Act applies in stages.
Duties for general-purpose AI models already apply. High-risk duties follow on the dates below.
Live now
GPAI obligationsRead more, GPAI obligations- Annex III high-risk systemsRead more, Annex III high-risk systems
- Annex I high-risk systemsRead more, Annex I high-risk systems
Fines for banned practices of up to €35,000,000 or 7% of total worldwide annual turnover, whichever is higher (Article 99(3)).
From repository scan to draft compliance dossier Three inputs, one compliance picture.
Static code scanning
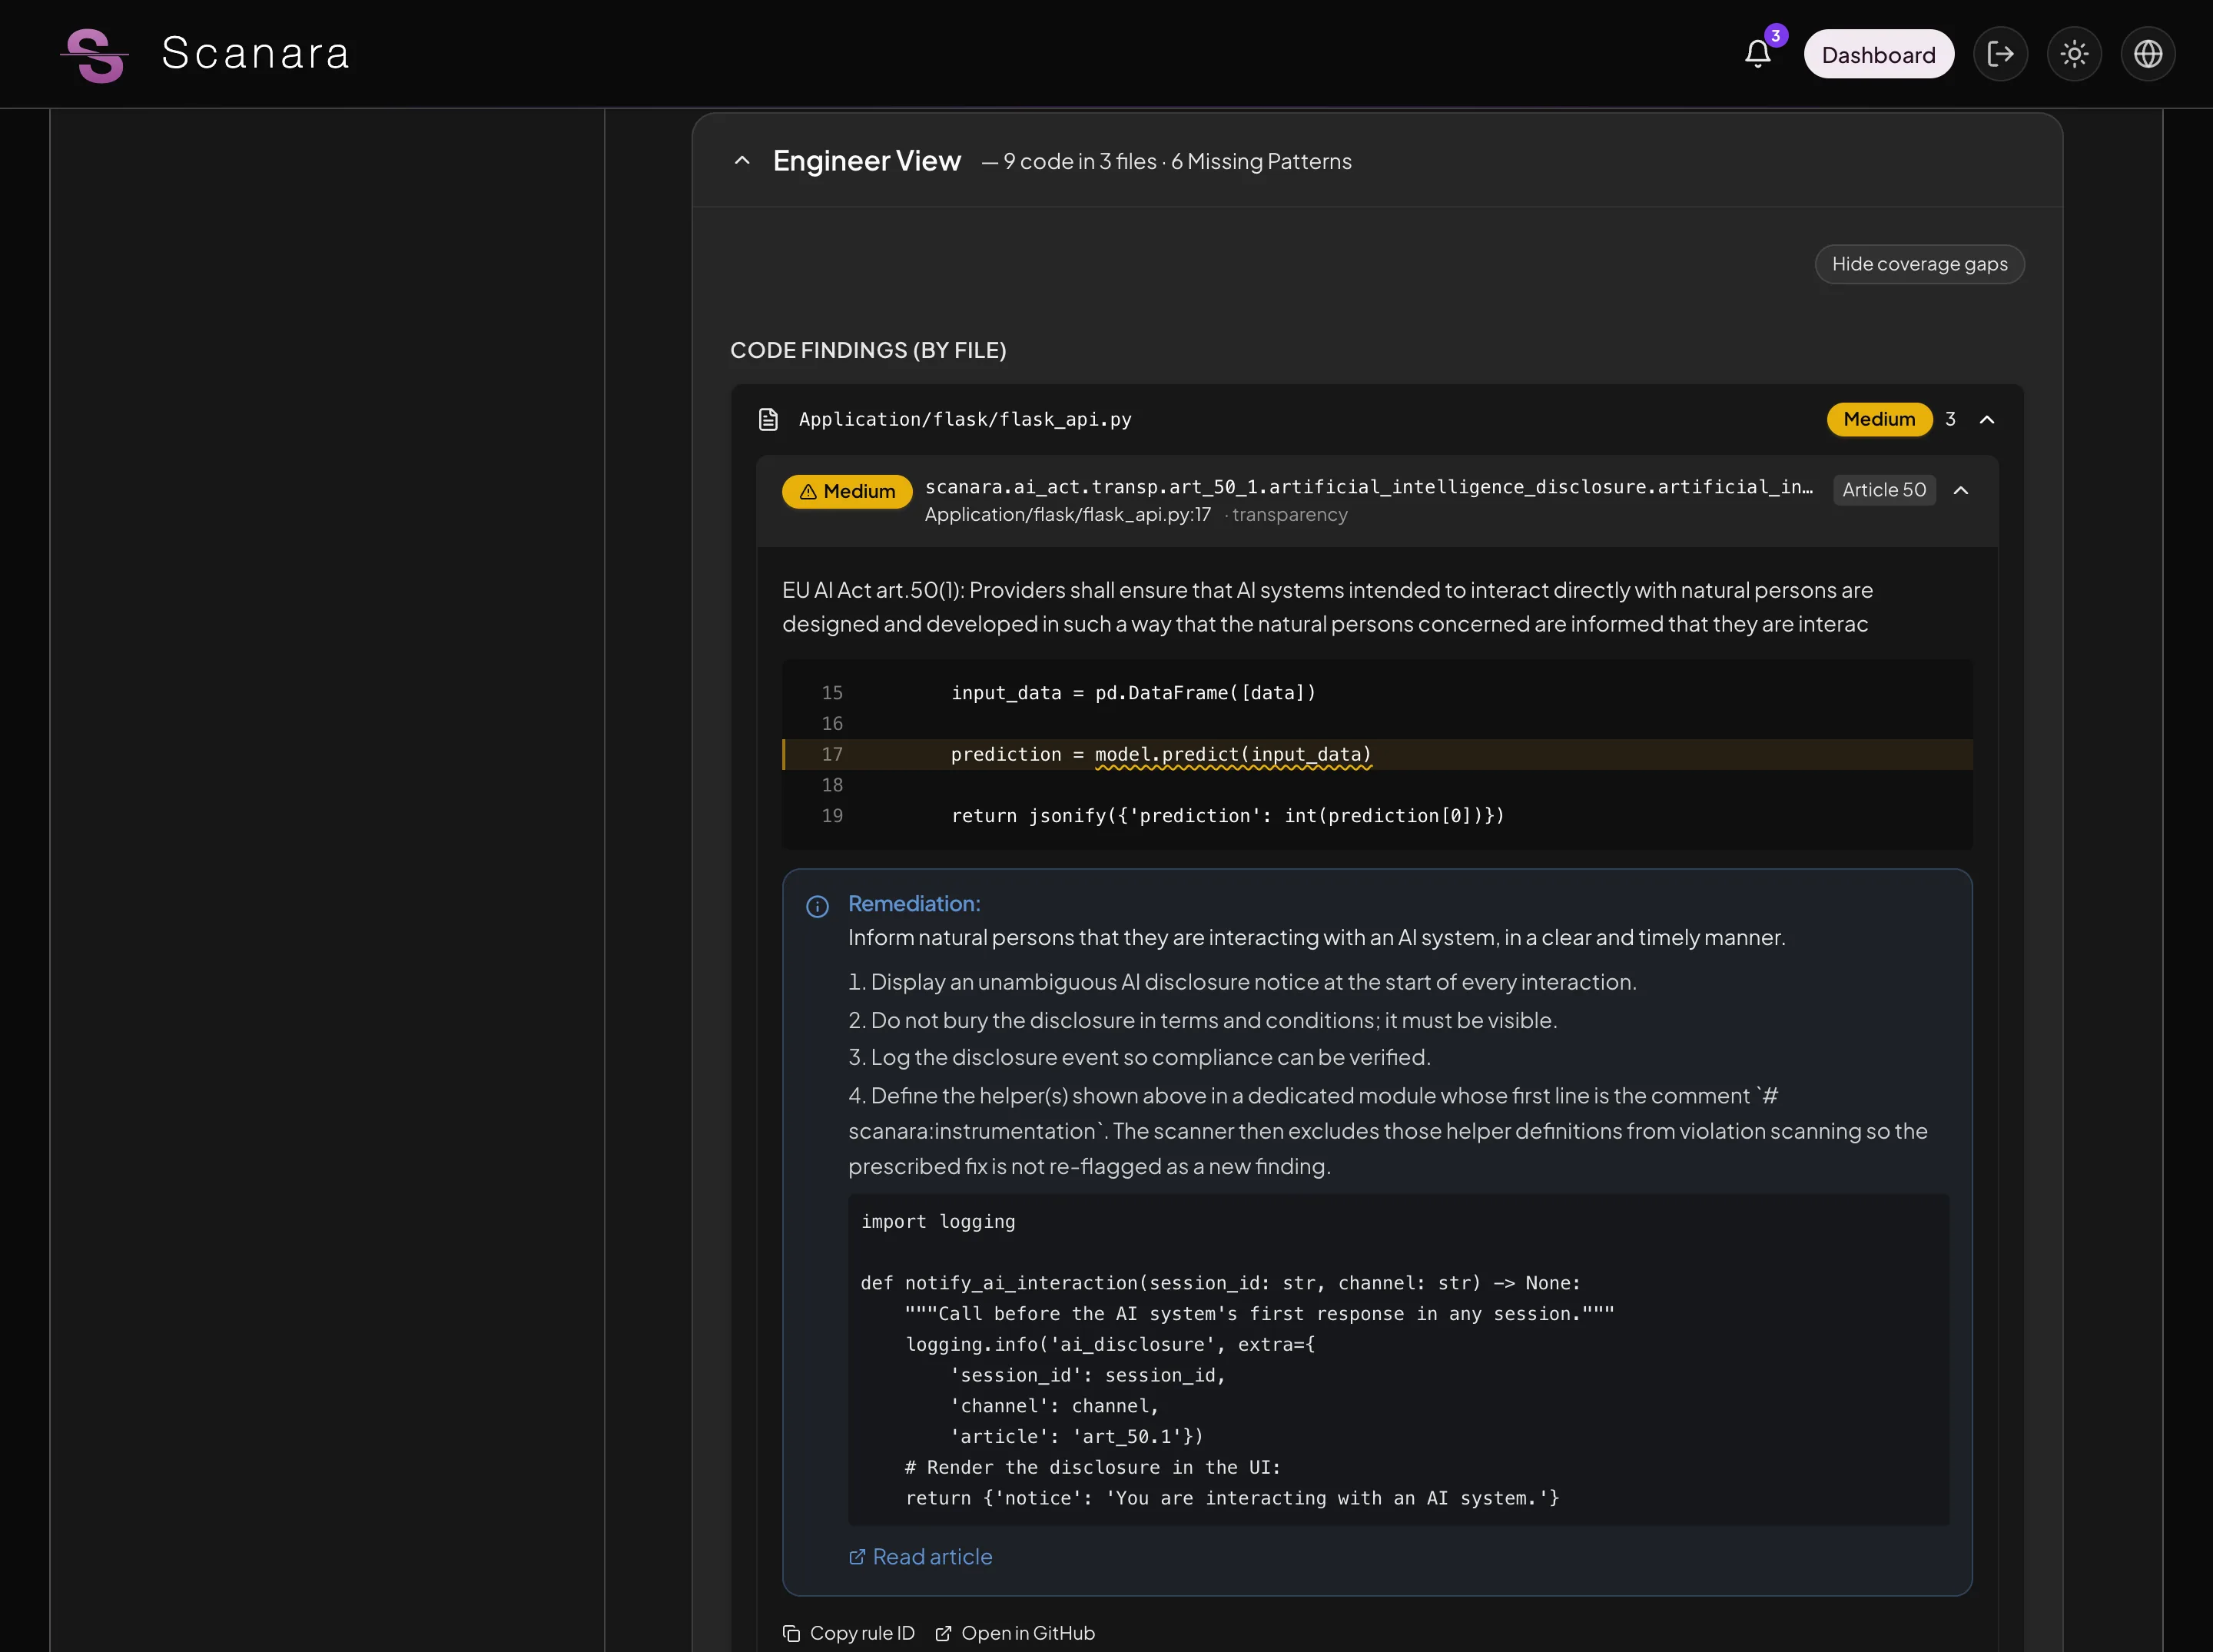
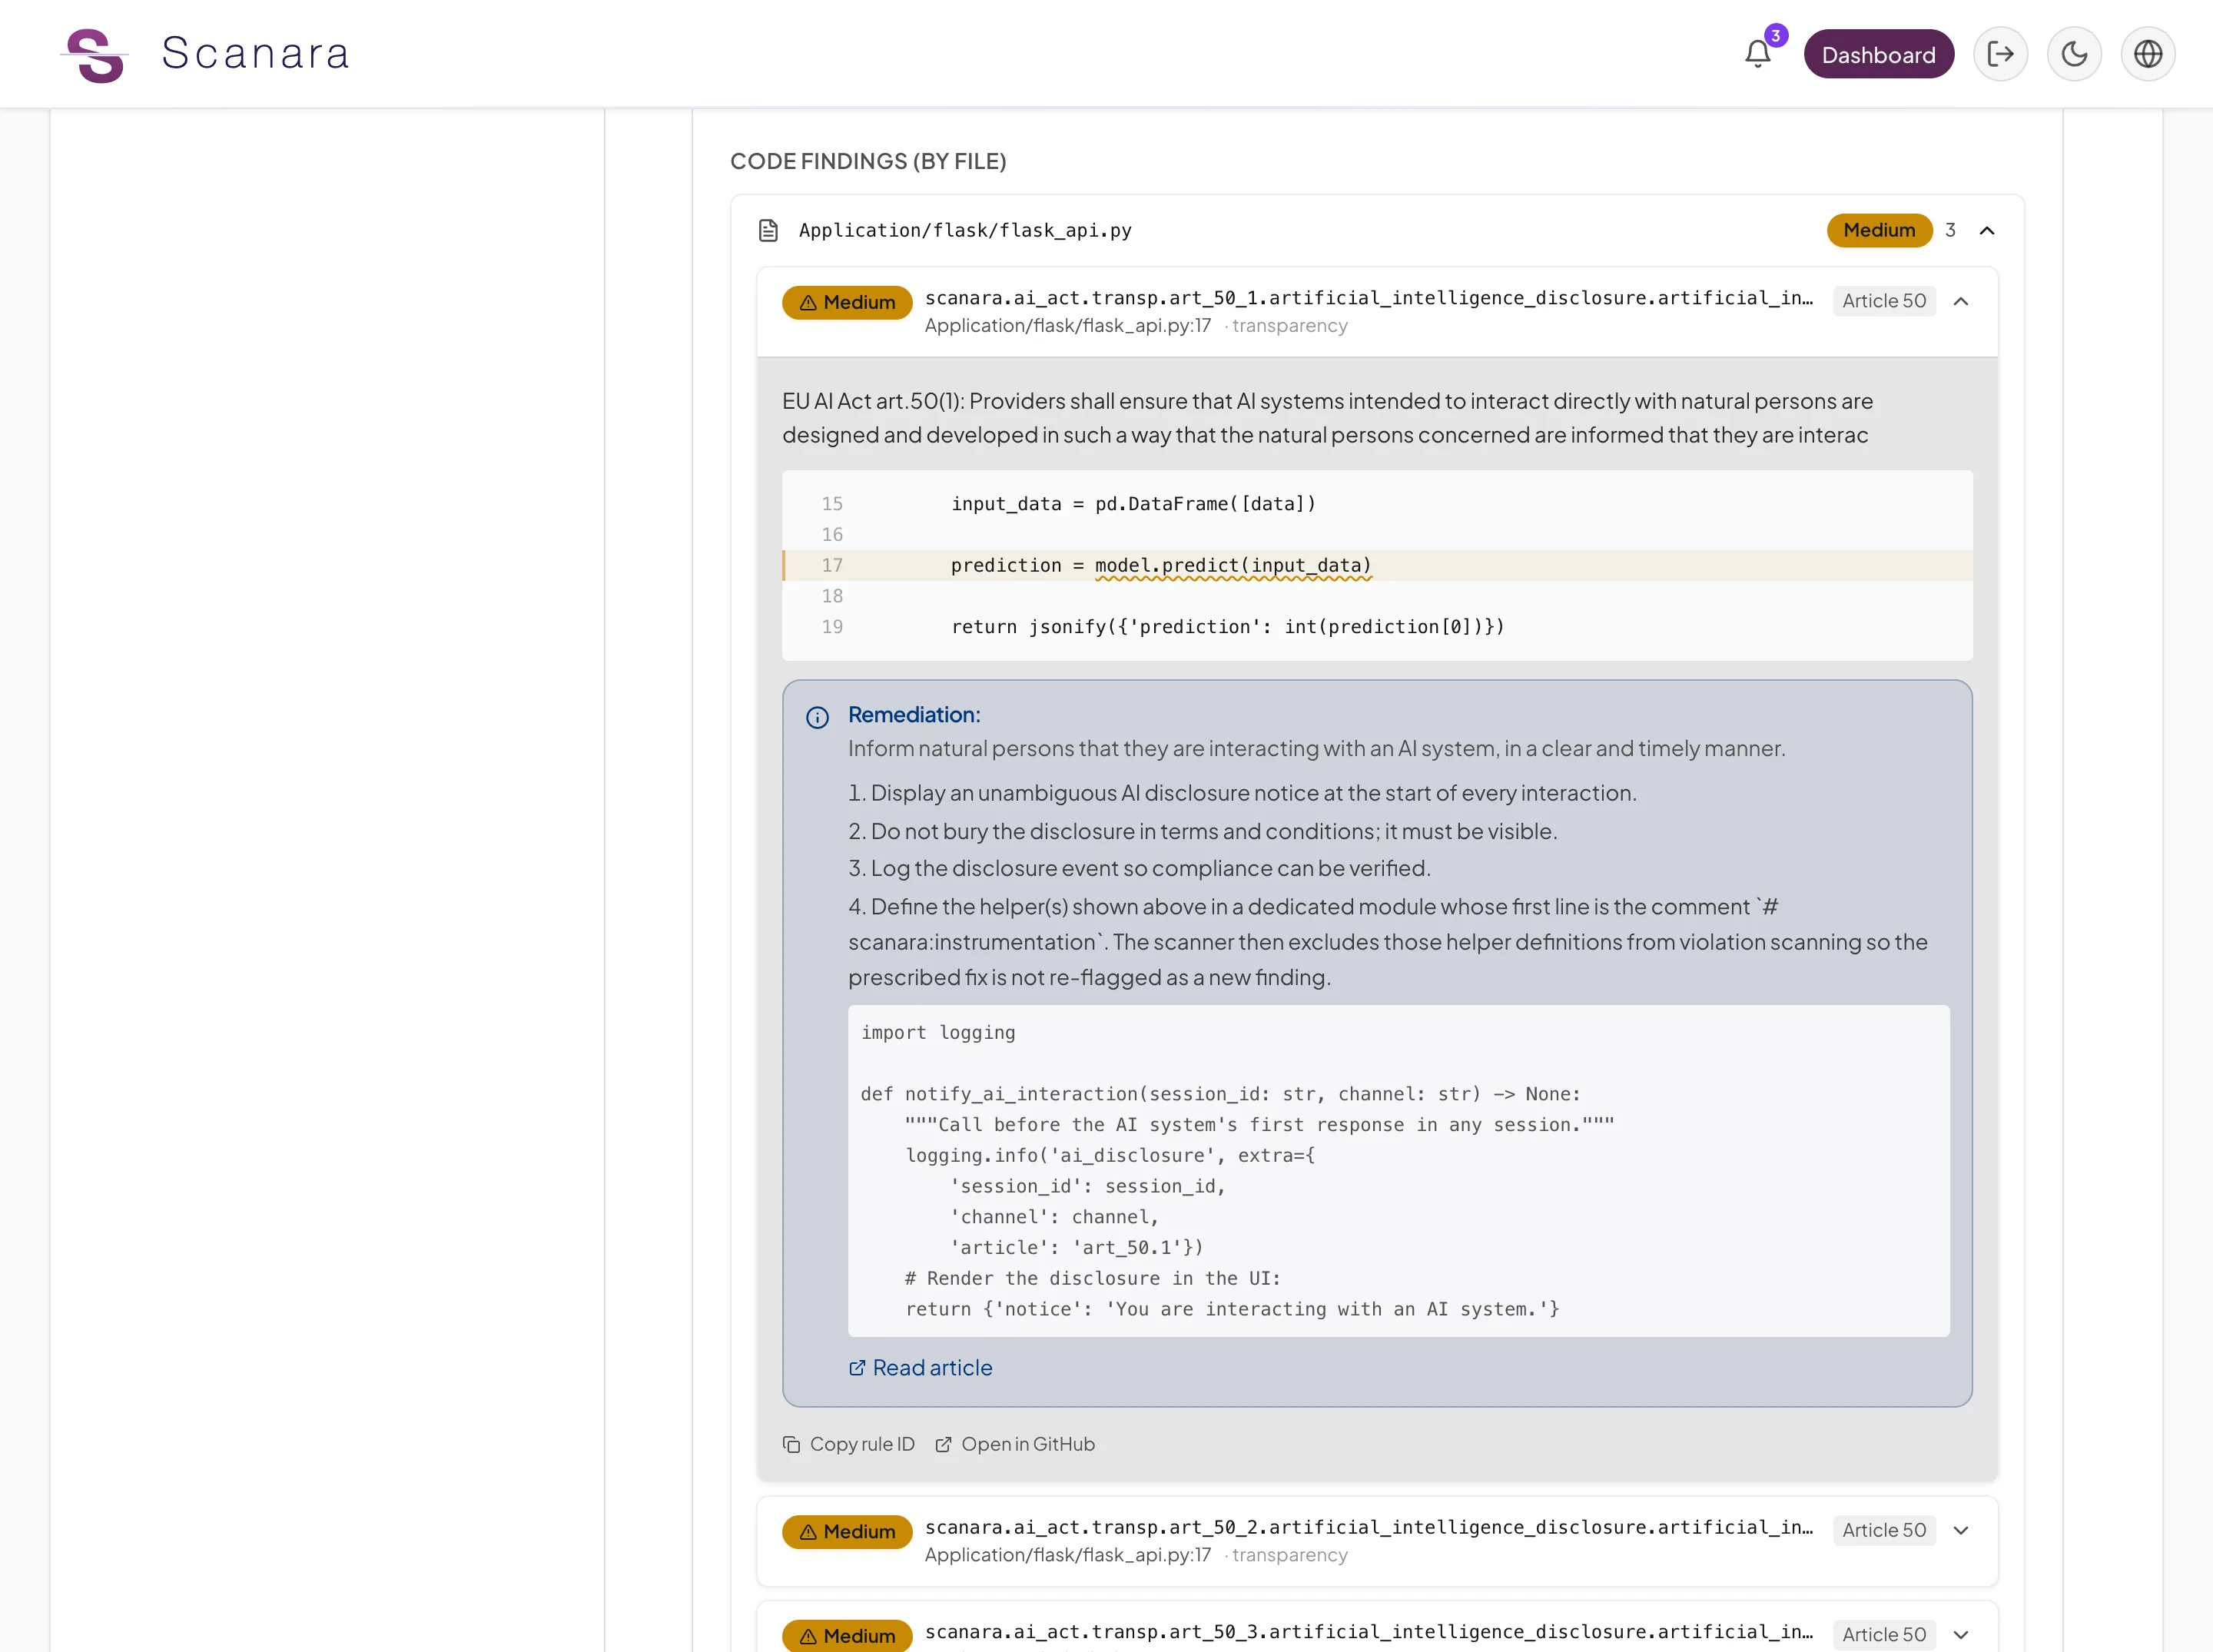
Scanning rules detect EU AI Act-relevant patterns directly in your source repositories — across 10+ programming languages, mapped to specific articles.
Document policy checks
A policy engine checks your technical documentation in 8 EU languages for the content the Act requires for your risk tier.
Structured assessments
Guided questionnaires cover what code can’t show: AI risk assessment (AIRA), FRIA, DPIA, GPAI provider duties, deployer duties and prohibited-practice screening.
The result: draft compliance documents
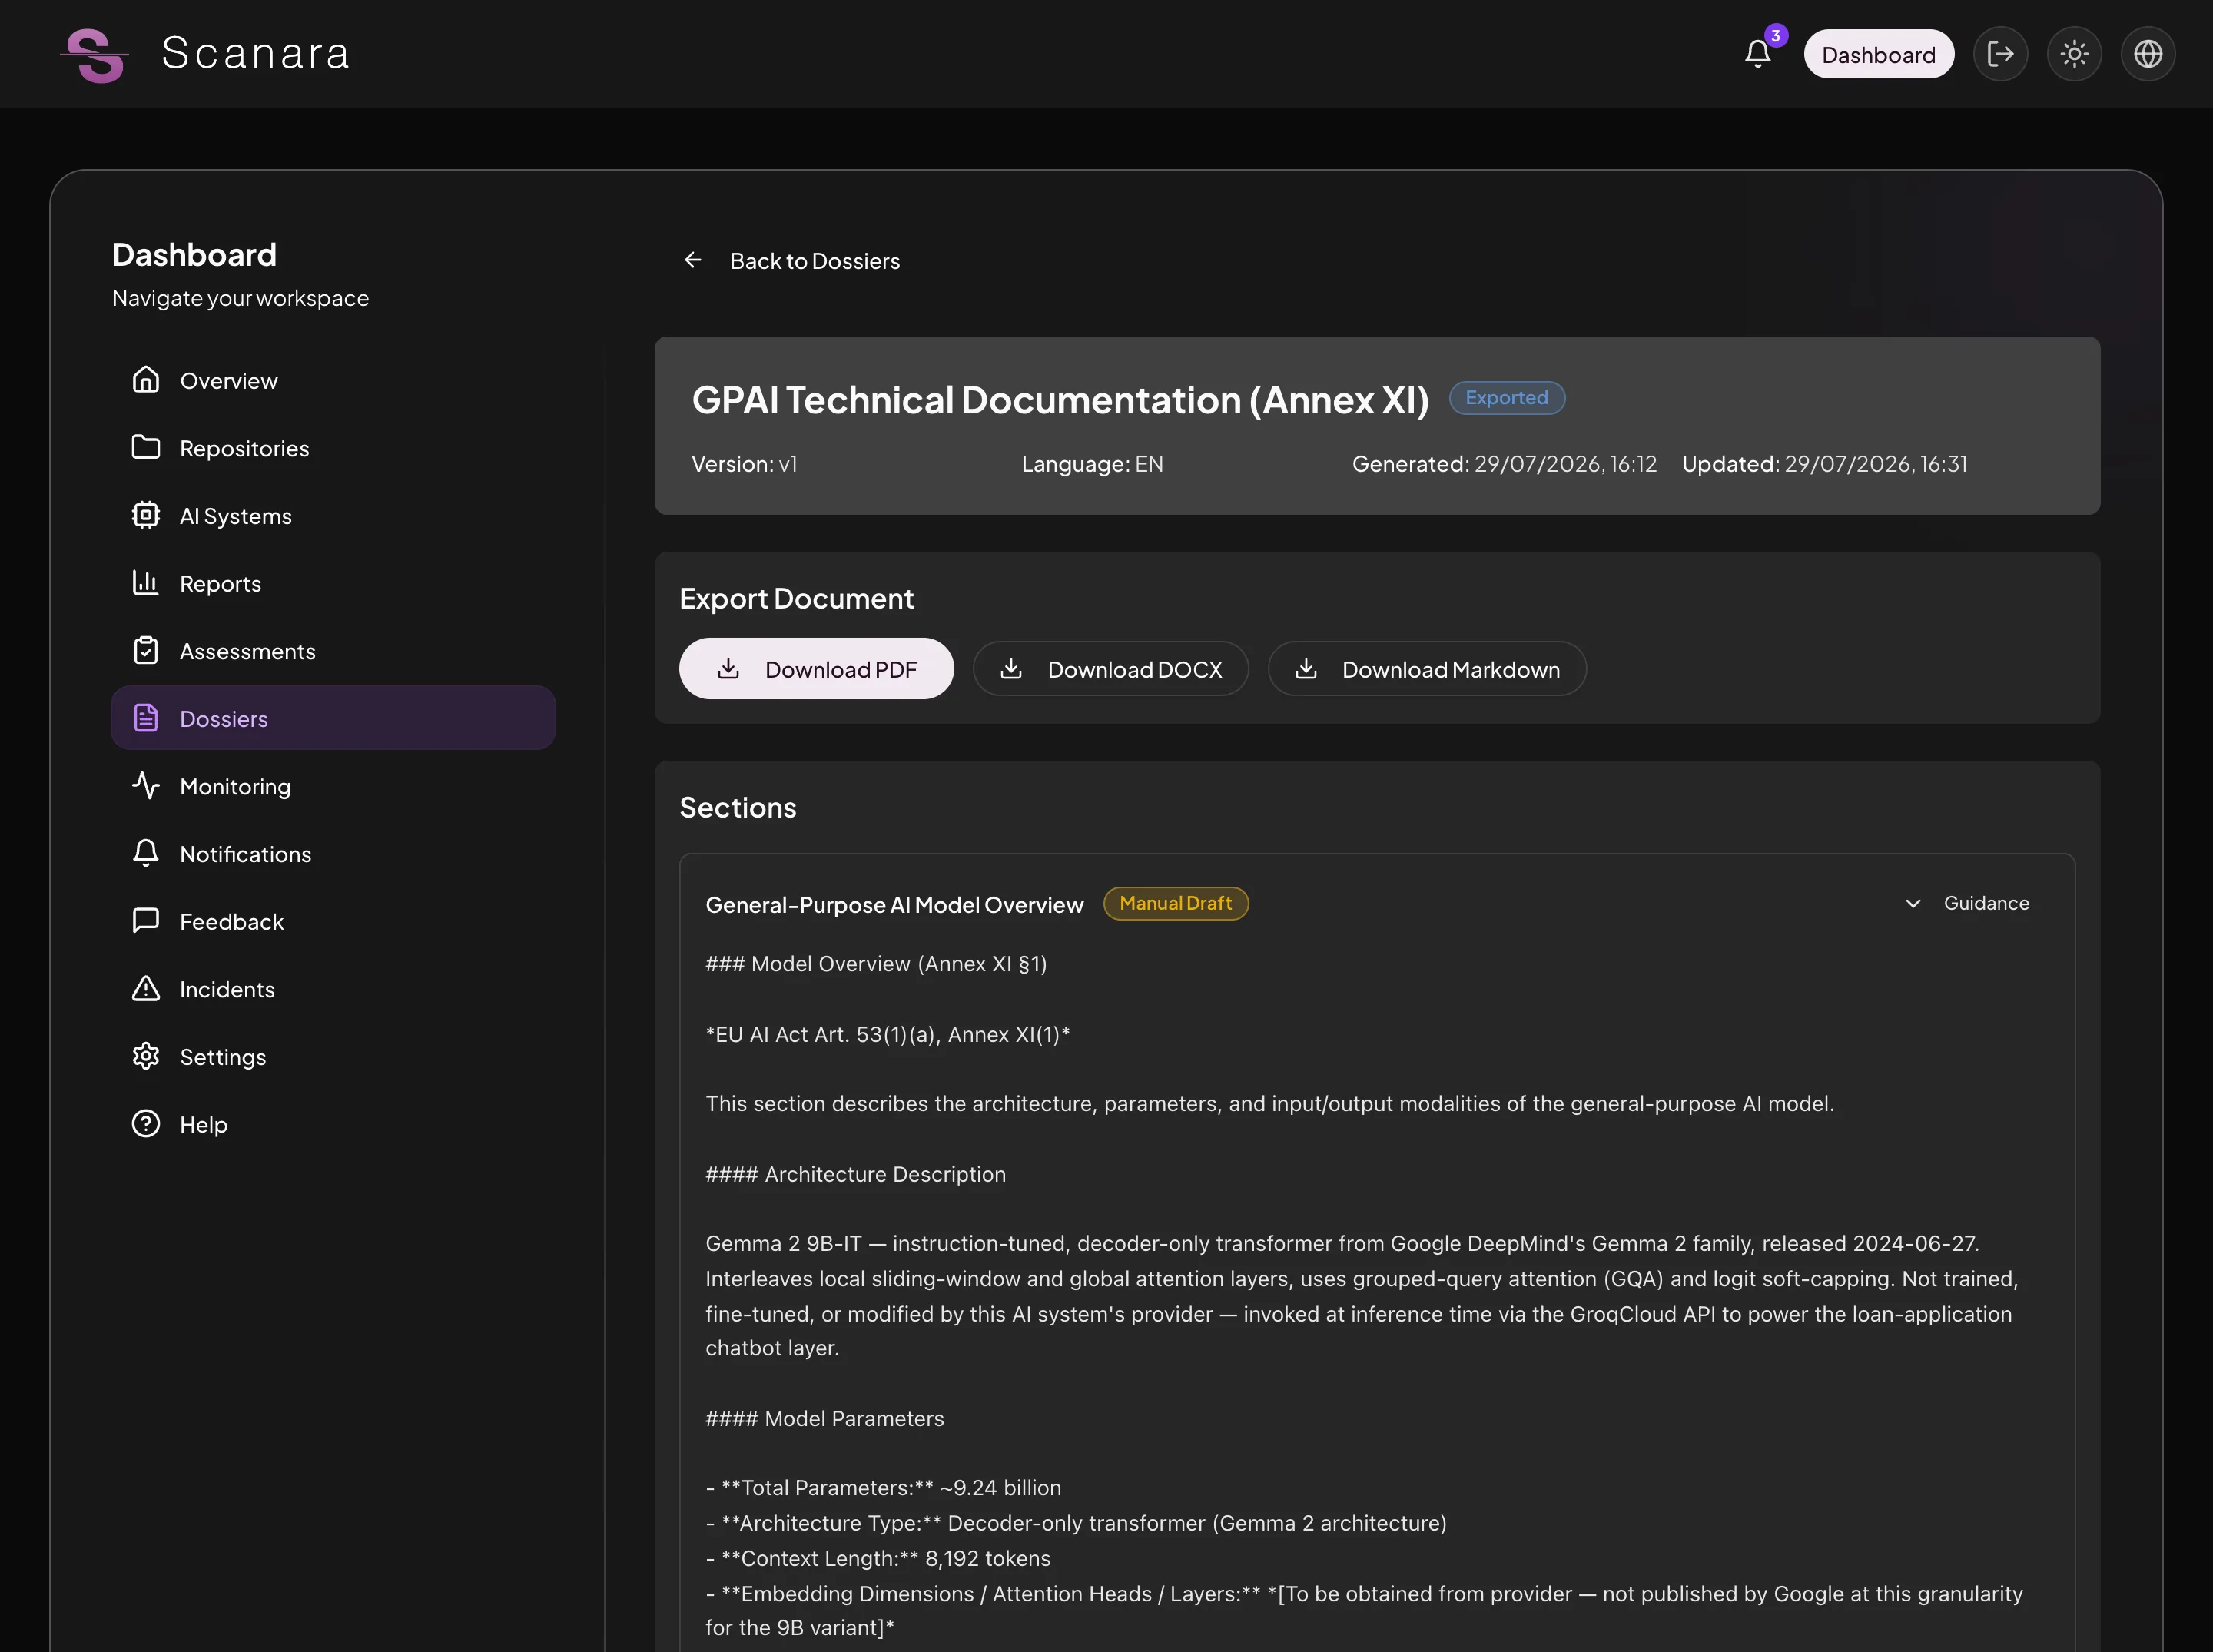
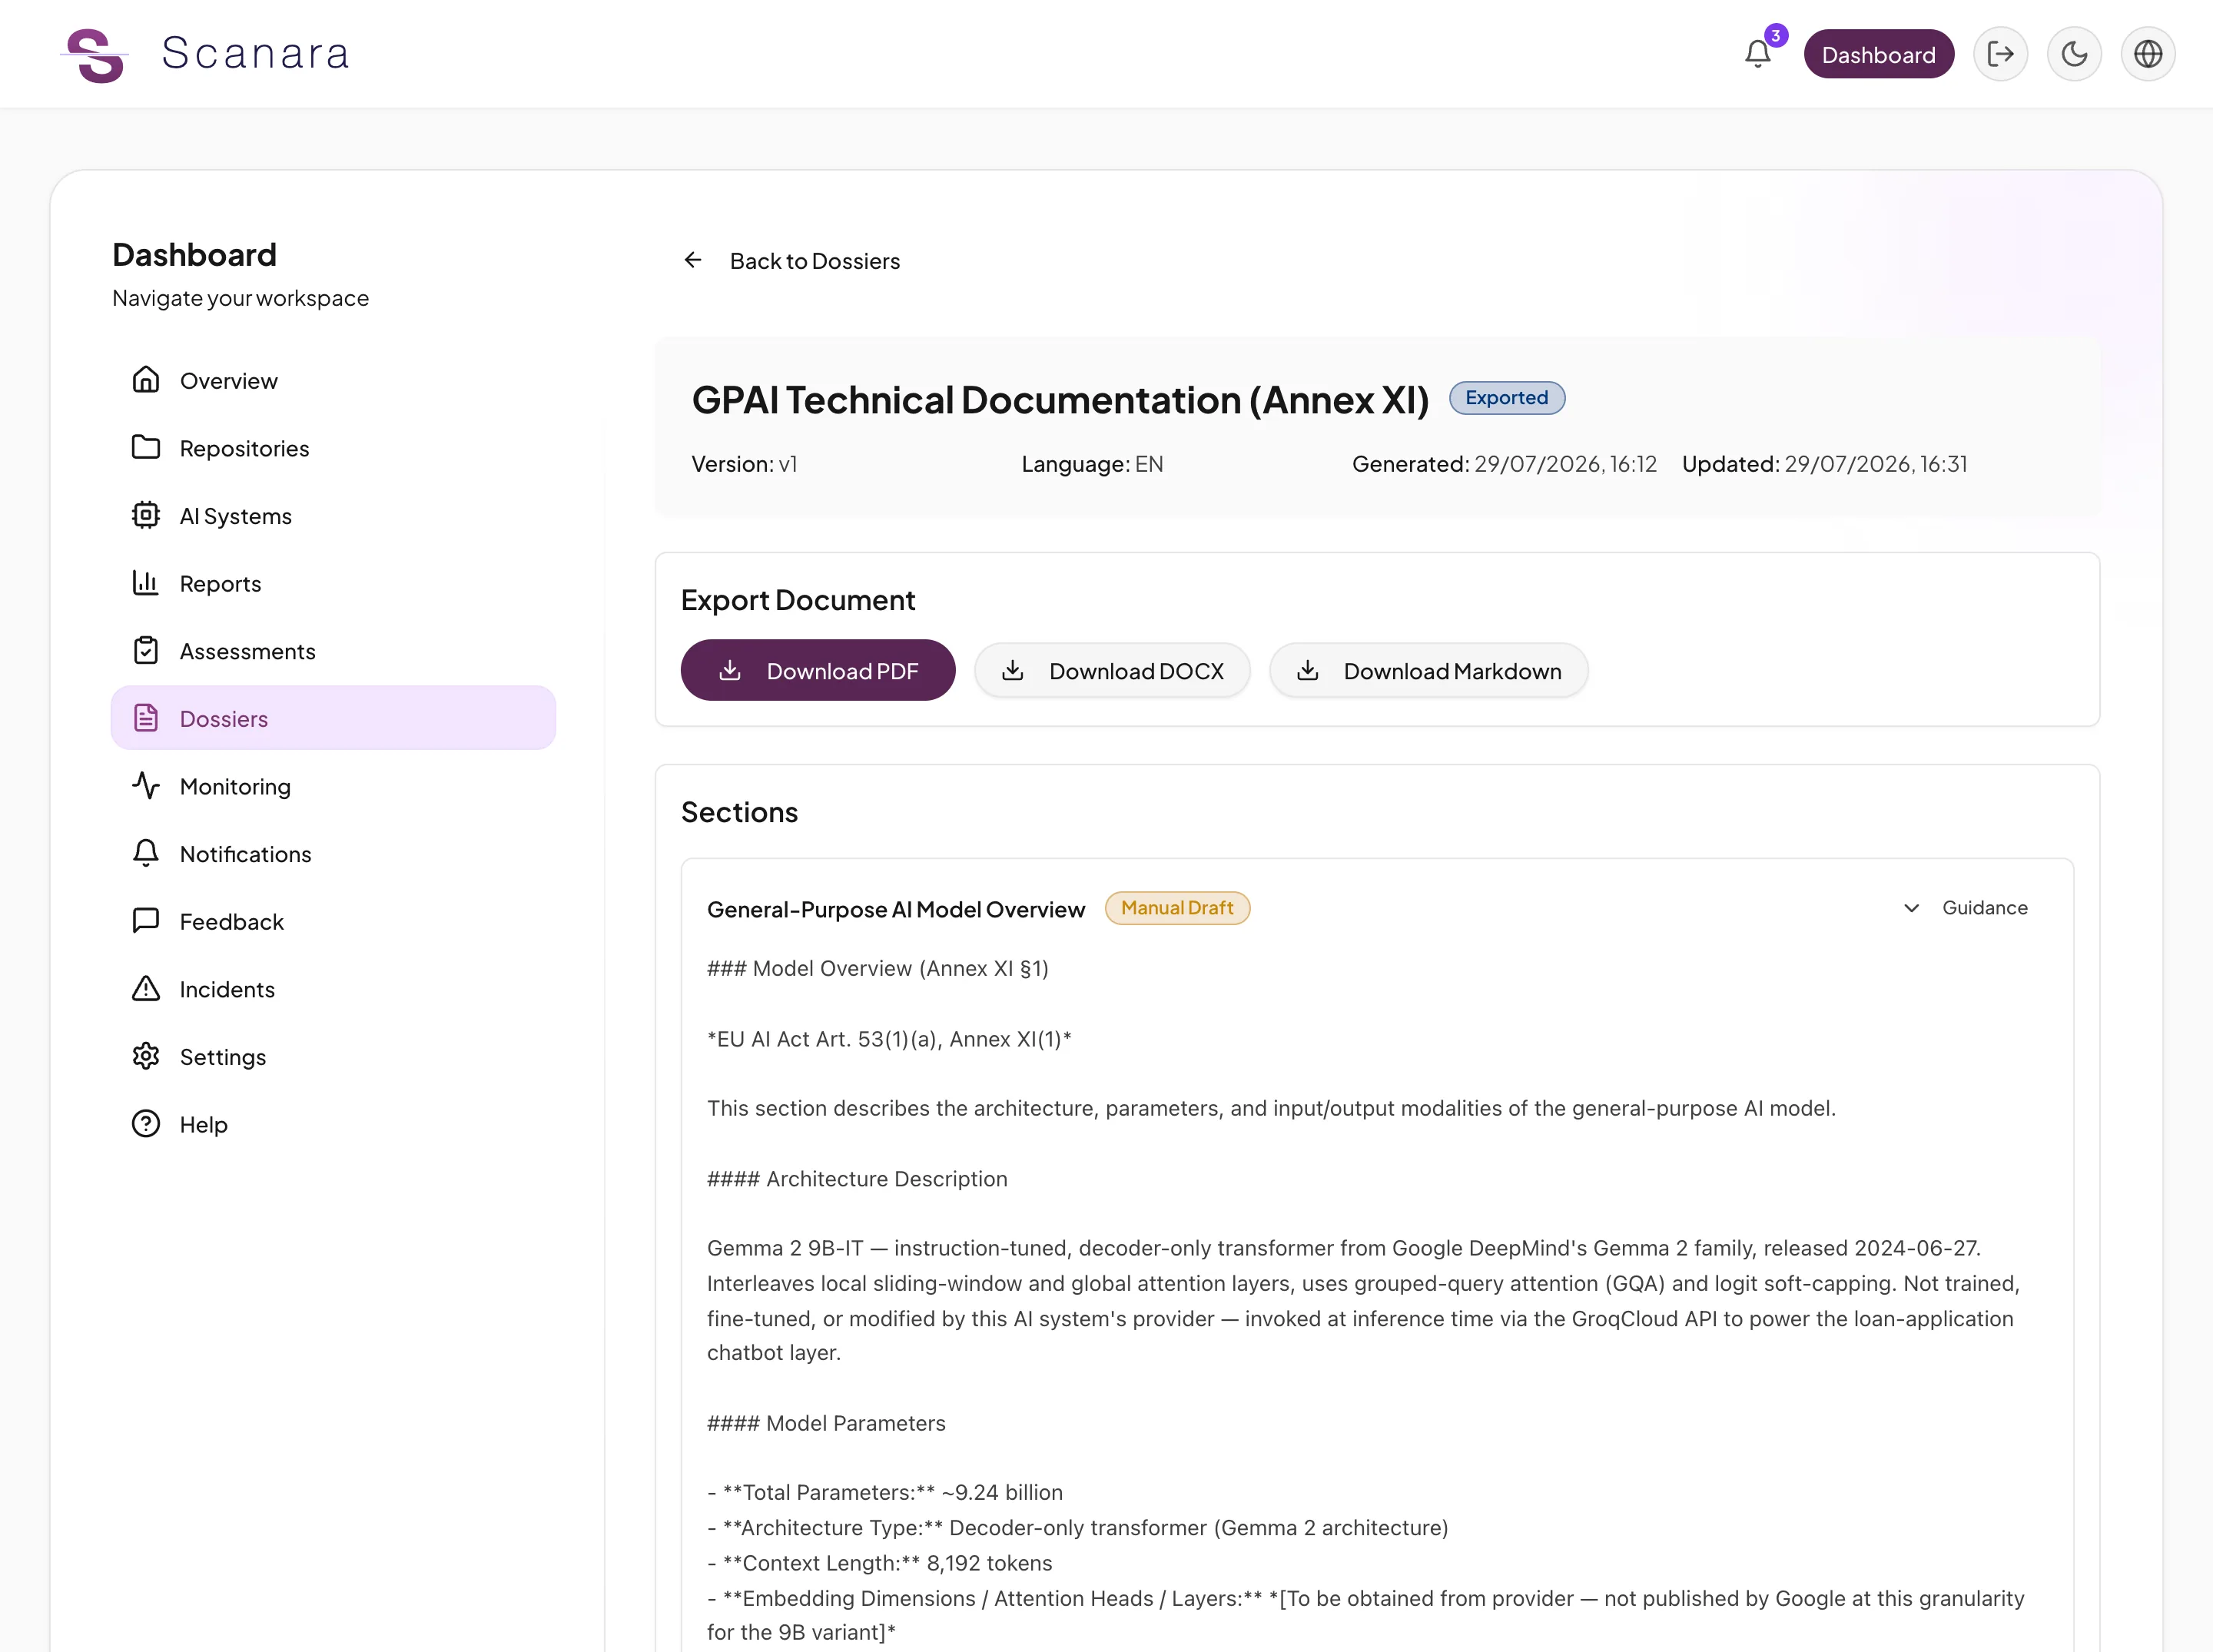
Scanara records a risk classification for each AI system and drafts the dossier: Annex IV technical documentation, Annex XI documentation for general-purpose AI models and the Annex V EU declaration of conformity. Registry data and assessment answers pre-fill the templates; you write the rest. Export as PDF, DOCX or Markdown.
Scanara supports your compliance work. It does not replace legal counsel or a notified body’s conformity assessment.
From repository to draft dossier in four steps
Step 1
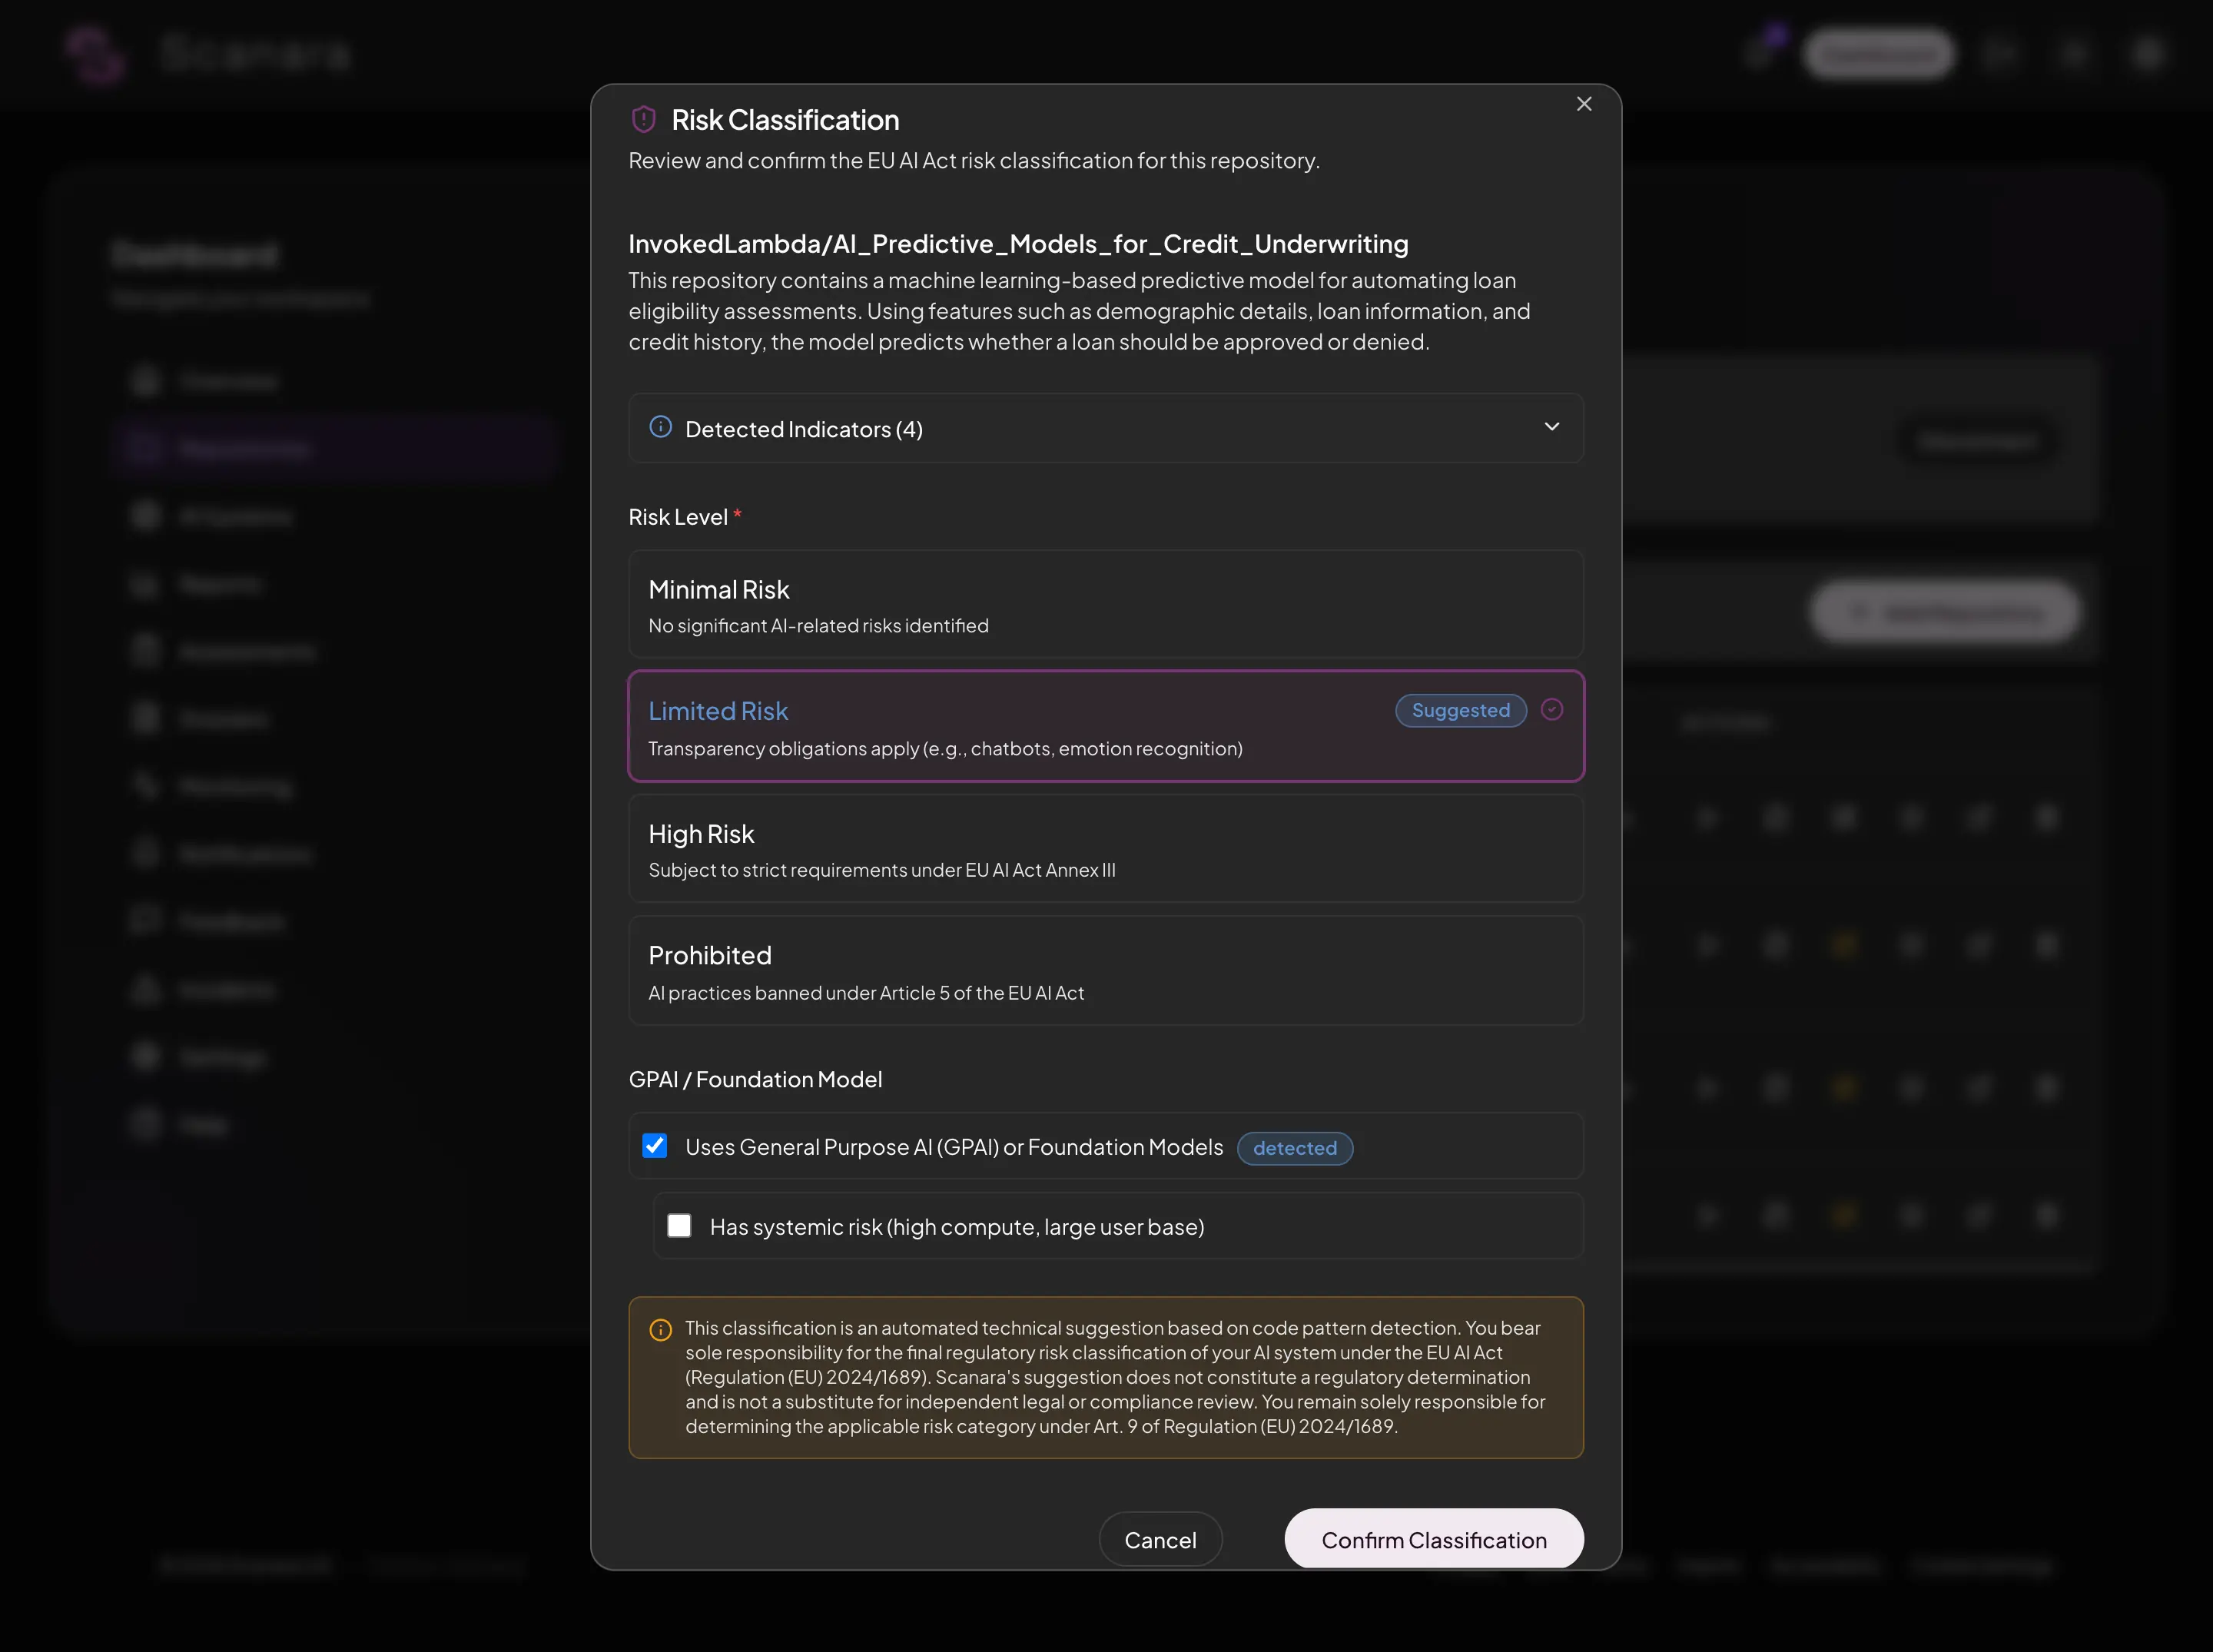
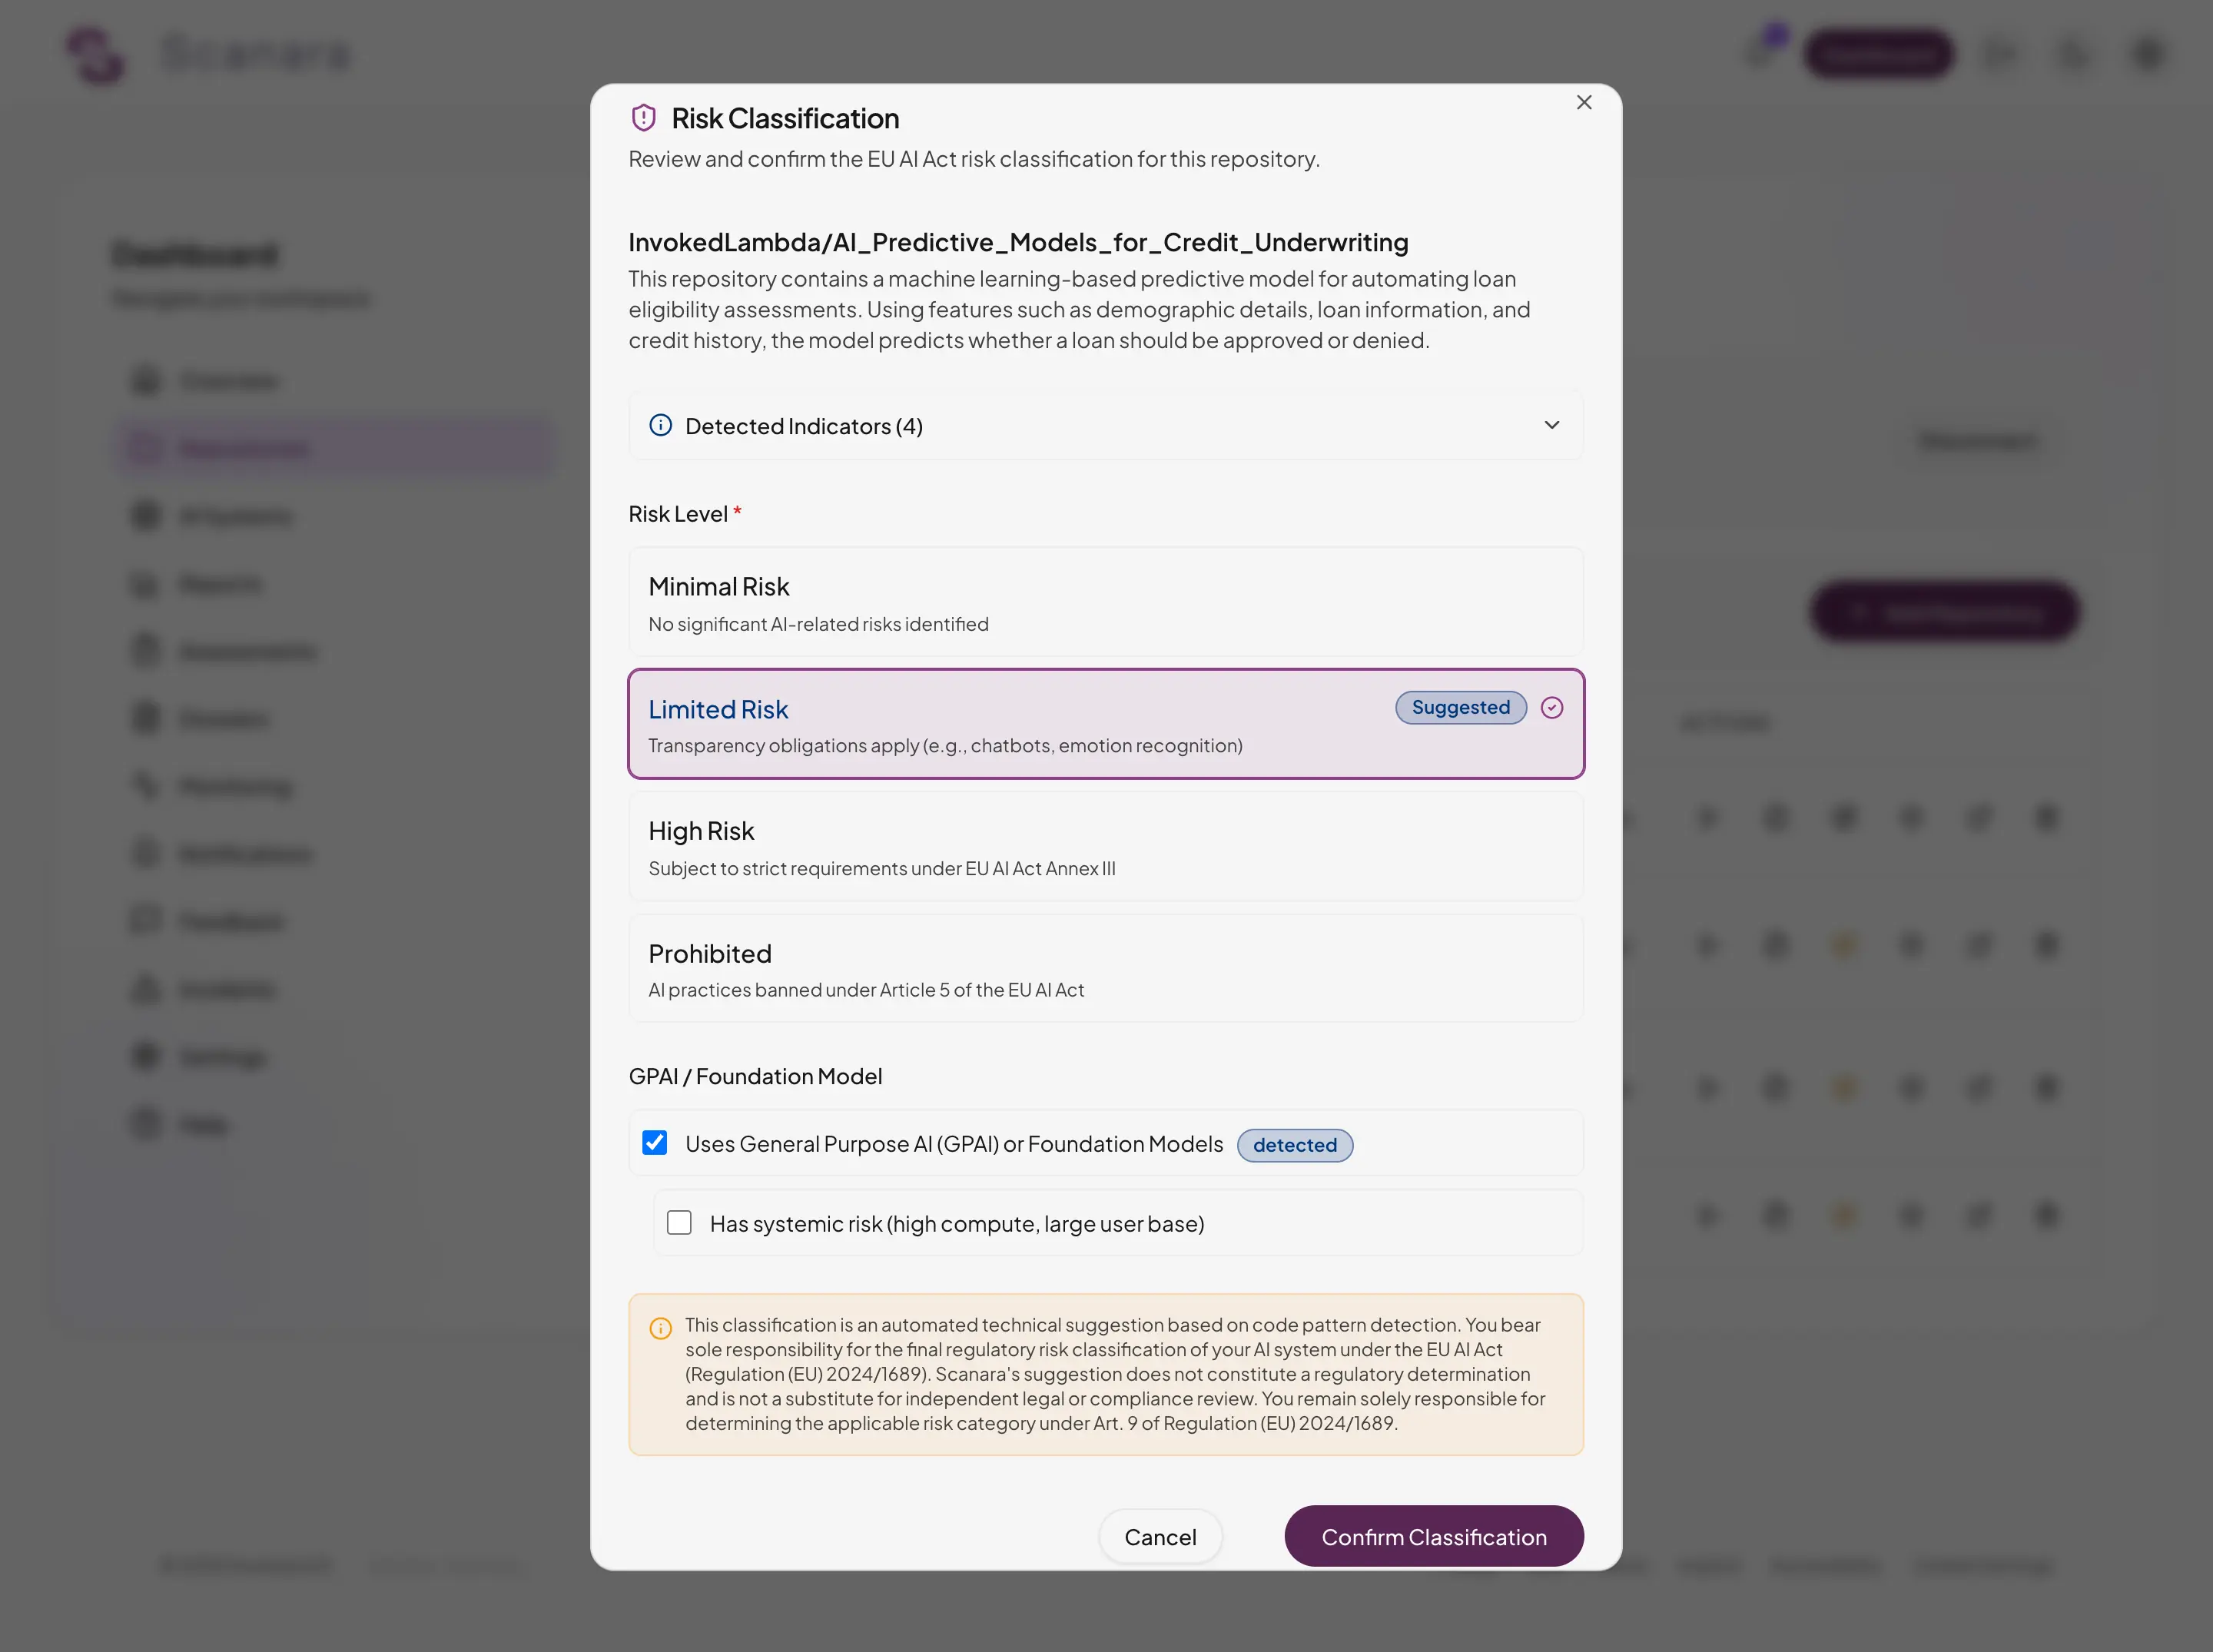
Risk classification
Scanara suggests a risk level for your GitHub repository and shows the indicators behind it. You confirm or change the classification.
Step 2
Connect
Create an AI system and link its repositories. Scanara suggests a risk classification for it; you confirm it.
Step 3
Scan
Dual-engine scanning: static analysis for code across 10+ languages, policy engine for documents in 8 EU languages. Every finding maps to a specific EU AI Act article.
Step 4
Report
Get your risk classification, compliance score and draft compliance dossier: Annex IV, Annex XI and Declaration of Conformity. Review and finalize them with qualified legal counsel.
Show prospects your compliance work
Scanara drafts the documents EU customers may ask for: risk classification, Annex IV technical documentation and scan results. Review and finalize them with your legal team before you share them.
A compliance tool that reads your actual code
Find code-level gaps before release
Generated scanning rules cover requirements of the Act that code or documents can show, each tied to an article. Guided assessments cover the rest. A scan result is not a compliance verdict.
Record a risk classification for every AI system
Scanara guides you through its four risk levels (prohibited, high, limited, minimal), including the Annex III categories, and documents your classification. You decide; Scanara structures and records it.
Generate draft dossiers from your data
Drafts of Annex IV technical documentation, Annex XI and the Declaration of Conformity, built from your scan results and assessment answers. Export as PDF, DOCX or Markdown.
Keep your evidence current
Every scan adds to a write-once audit log. The GitHub App can run a compliance check on every pull request.
Built on the regulation itself — not a summary of it
Every rule anchored to its exact legal source.
- 119 + 14
- article IDs and annexes in the consolidated text (27 July 2026)
- 12
- programming languages, with a confidence level per language
- 54
- test applications re-verified before every release
Every finding cites the EU AI Act article it relates to.
Each release is verified against fixture tests, golden outputs, and coverage KPIs before any rule ships.
Security and data handling
EU Data Residency
Customer data — source code, scan results, assessments, dossiers — stored and processed in AWS eu-west-1 (Dublin, Ireland).
Scanara UG, Dachau
German company (Scanara UG, haftungsbeschränkt) based in Dachau, Germany.
Write-once Audit Trail
A write-once (WORM) log of scans and actions.
EU-First Billing
SEPA & credit card support with EUR billing.
We don't keep a copy of your repository
Files are read from GitHub, scanned in an isolated function, and discarded. Findings keep only the flagged lines and their immediate context. Scanara does not keep a full copy of your repository (Privacy Policy §2.3).
How we handle your code — Privacy Policy §2.3Start free, upgrade when you need more
Prices include VAT. Free plan limits are one-time totals; paid plan limits reset every month. Scanara starts at €0.
Free
For individual developers exploring EU AI Act compliance.
- 5 scans (lifetime)
- 1 AI system (lifetime)
- 2 repositories (lifetime)
- 1 team member
- 3 assessments (lifetime)
- 2 dossiers (lifetime)
- 30-day scan history
Team
For small teams that build AI systems and start their EU AI Act work.
incl. VAT
- 100 scans/month
- 10 AI systems
- 15 repositories
- 7 team members
- 20 assessments/month
- 10 dossiers/month
- Merge gate (1 repo)
- 90-day audit trail
No credit card required for the Free plan
Find out which EU AI Act articles apply to your code
Start a free scan and get a first report with article-level findings.